← 返回列表

Adversary research you can operationalize today

单站 Rapid7 Blog 作者 Rapid7 入库 2026-11-17T04:03:01

Disclosures doubled

High- & critical-severity CVEs year-over-year - 8,539 vs 4,268 in Q2 2025

Holy grail flaws

Of exploited vulnerabilities required no auth and no user interaction (25 of 40)

U.S. victims

Ransomware leak-site listings in the U.S. - roughly 9× Germany, the next country

Underground listings

Exploit & access listings across 20 dark web sources, 23 CVEs actively traded
Disclosures doubled

High- & critical-severity CVEs year-over-year - 8,539 vs 4,268 in Q2 2025

Holy grail flaws

Of exploited vulnerabilities required no auth and no user interaction (25 of 40)

U.S. victims

Ransomware leak-site listings in the U.S. - roughly 9× Germany, the next country

Underground listings

Exploit & access listings across 20 dark web sources, 23 CVEs actively traded

quarterly-threat-landscape-report.webp

Quarterly Threat Landscape Report Q3 2026

Ungated research, no sign up required.

Latest from the Intelligence team

WebcastInside the First 60 Minutes of an AttackNovember 18, 2026Virtual
BrightTalk Website Thumbnails (11).png

Exposure ManagementPatch Tuesday - November 2026
patch-tuesday.jpeg

Vulnerabilities and ExploitsCritical vulnerabilities in N-able N-central prompt hosted shutdown

ETR-repeated.webp

Play videoPodcastHacktics & Telemetry, E18: Microsoft Edge 0-Click & Kubernetes AI Security (ft. Derrick Sutherland)

Hacktics & Telemetry, E18: Microsoft Edge 0-Click & Kubernetes AI Security (ft. Derrick Sutherland)

Vulnerabilities and ExploitsAdditional Ivanti Connect Secure zero-days exploited in the wild (CVE-2026-111357, CVE-2026-118527)

ETR-repeated.webp

Vulnerabilities and ExploitsRapid7 Analysis: Unauthenticated File Upload to RCE in BeyondTrust Remote Support (CVE-2026-102764)

rapid7-logo-blue-glow.jpg

MetasploitMetasploit Wrap Up: Langflow, MongoDB, and More
metasploit-sky.png

Threat ResearchQ3 2026 Threat Update: Attackers Are Exploiting Vulnerabilities Within 3 Days
Copy of Rapid7 intelligence report template.png

Vulnerability and Exploit Database

Rapid7’s curated database of vulnerabilities, featuring exploit modules and check methods integrated into the Metasploit Framework.

Rapid7 Intelligence, built in

Rapid7 Intelligence powers a suite of open-source tools used by security researchers, pen testers, and threat hunters worldwide. Continuously updated by the community and feeding directly into the Rapid7 Platform.
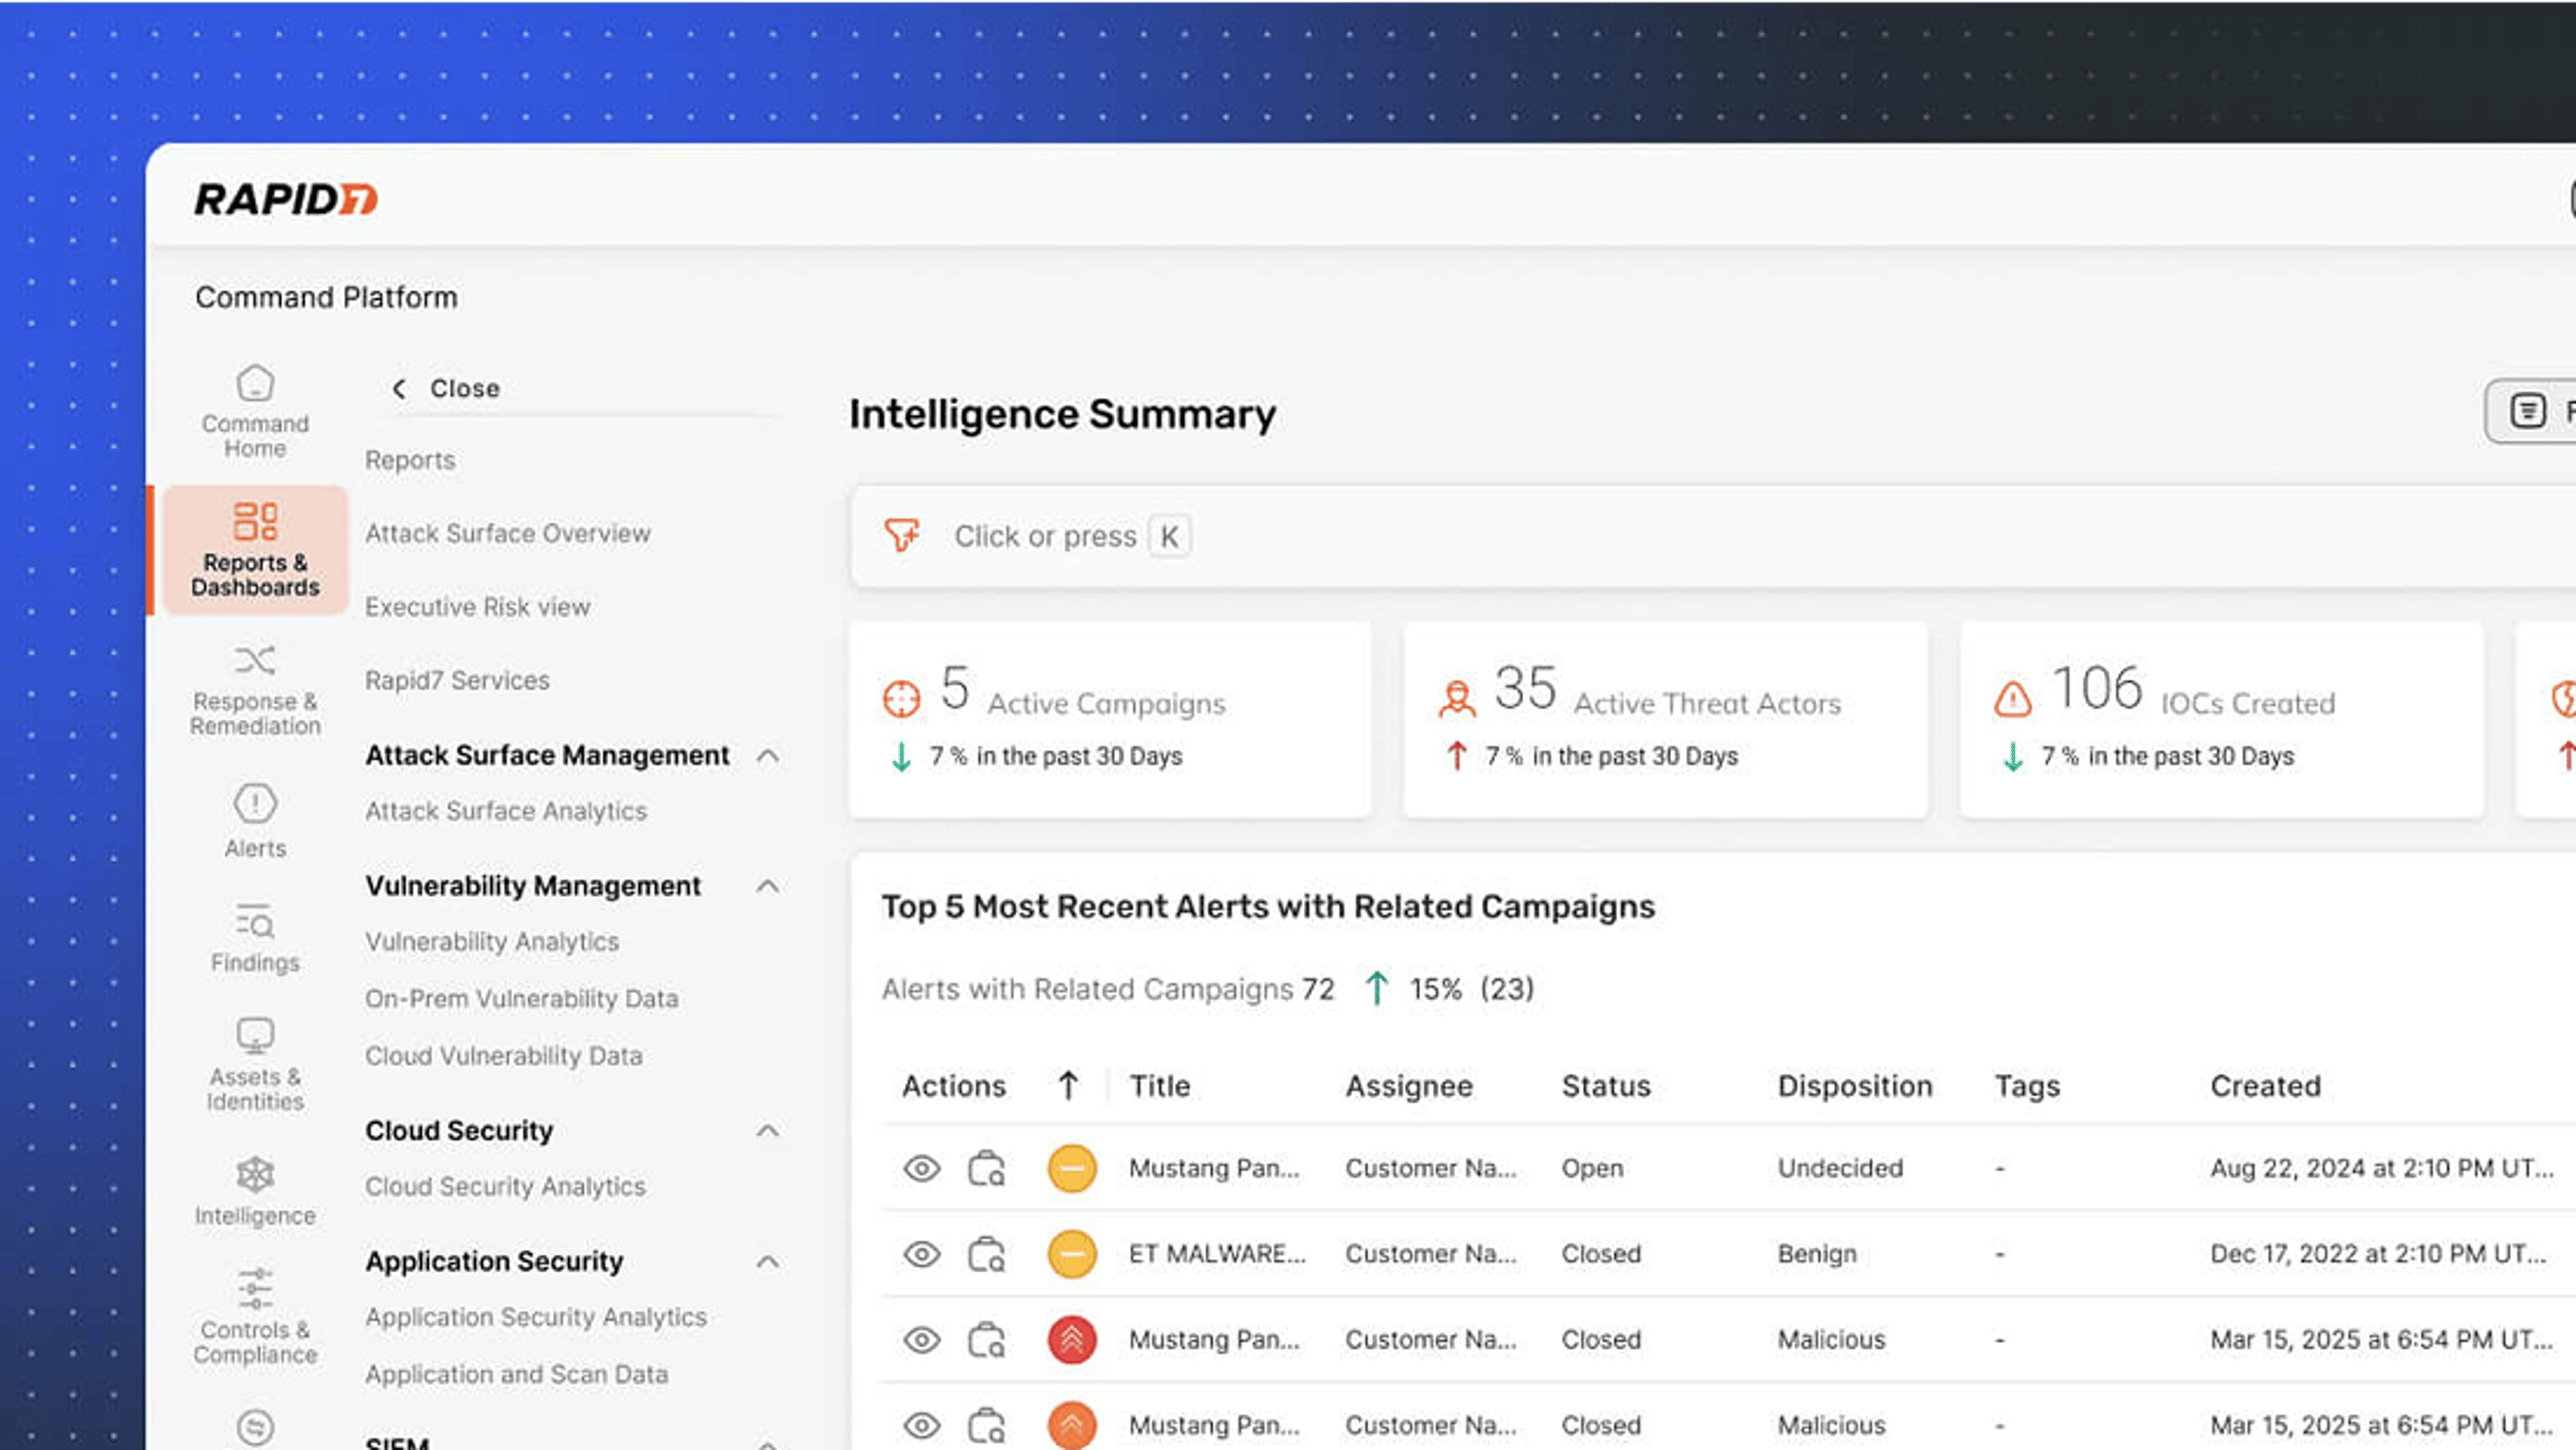
Threat Intelligence ServicesCurated, actionable intel that accelerates response across your SOC.Learn more

Threat Intelligence Services

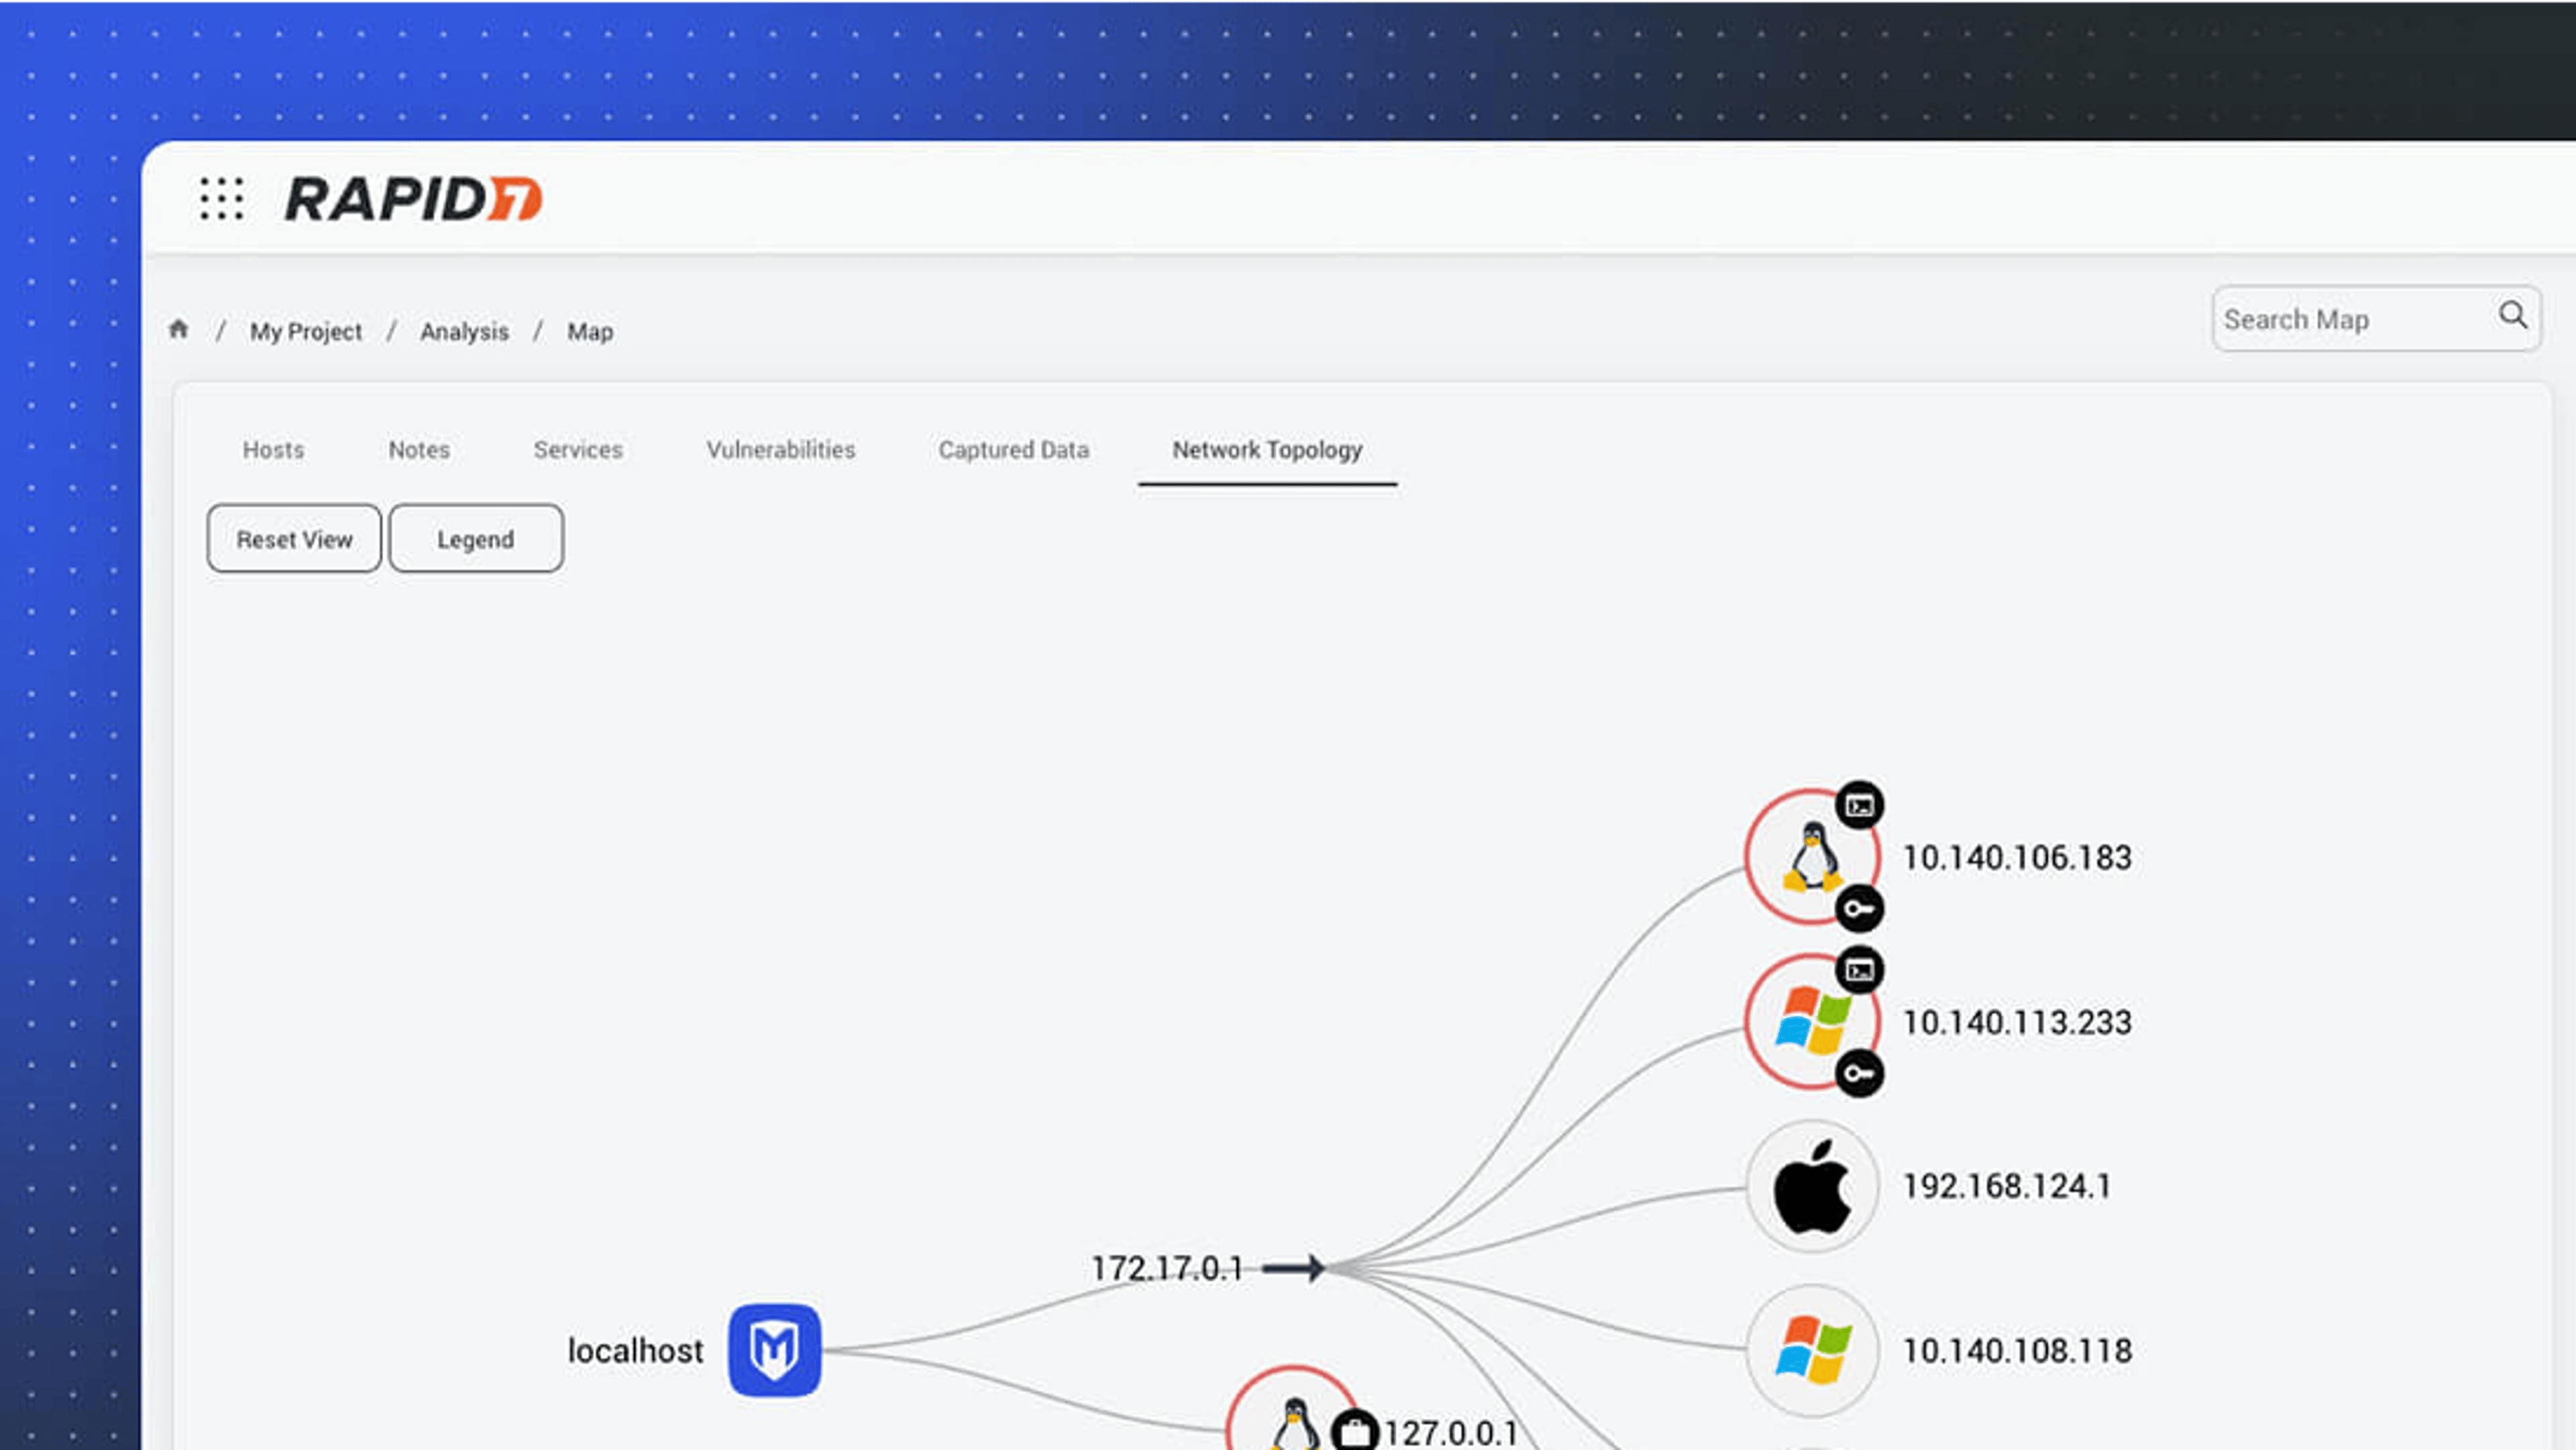
MetasploitThe world's most widely used penetration testing framework, helping security teams verify vulnerabilities and manage risk-aware assessments.Learn more

Metasploit

VelociraptorAn advanced open-source digital forensics and incident response platform for hunting threats across enterprise endpoints at scale.Learn more

Velociraptor

Project SonarA security research project that conducts internet-wide surveys to gain insights into global exposure to common vulnerabilities.Learn more

Project Sonar

Threat Intelligence ServicesCurated, actionable intel that accelerates response across your SOC.Learn more

Threat Intelligence Services

MetasploitThe world's most widely used penetration testing framework, helping security teams verify vulnerabilities and manage risk-aware assessments.Learn more

Metasploit

VelociraptorAn advanced open-source digital forensics and incident response platform for hunting threats across enterprise endpoints at scale.Learn more

Velociraptor

Project SonarA security research project that conducts internet-wide surveys to gain insights into global exposure to common vulnerabilities.Learn more

Project Sonar

Research is only half the loop

Every Intelligence finding feeds the Command Platform, so the CVEs and detections here become prioritisation and hunts you can action.

原文链接:https://www.rapid7.com/research/