BLog & News
News,Press & Research
Security research, product updates, and insights from the team building the AI-Native SDLC Defense Platform.
Featured Post
News
November 4, 2026
BoostSecurity Joins Microsoft for Startups Pegasus Program as AI Reshapes How Software Is Built and Attacked
Following PHP2Shell, Montreal startup brings agentic development security to Microsoft's enterprise customers
Read Article
Latest Posts
Blog ArticlesGo Supply Chain Security in BriefGo's decentralized module system and checksum verification reduce some supply chain risks familiar from npm. They do not establish whether a dependency is trustworthy: misleading module paths, repository ownership changes, and proxy-vs-source mismatches remain real attack vectors.November 2, 2026
Blog ArticlesIncident Response Playbook for Your Next Supply Chain AttackWork through three supply chain incident scenarios: a compromised dependency, a pull request crossing a trust boundary, and insider misuse. Includes a practical, two-page response checklist.October 30, 2026

AppSecSix Months After Acquiring SecureIQx, We’re Shipping ThreatRank in Boost ASPMSix months ago, Boost acquired SecureIQx. Today we’re shipping the technology that team built, ThreatRank, inside Boost ASPM. ThreatRank tells you whether your code can reach each open-source CVE in a repository.October 19, 2026

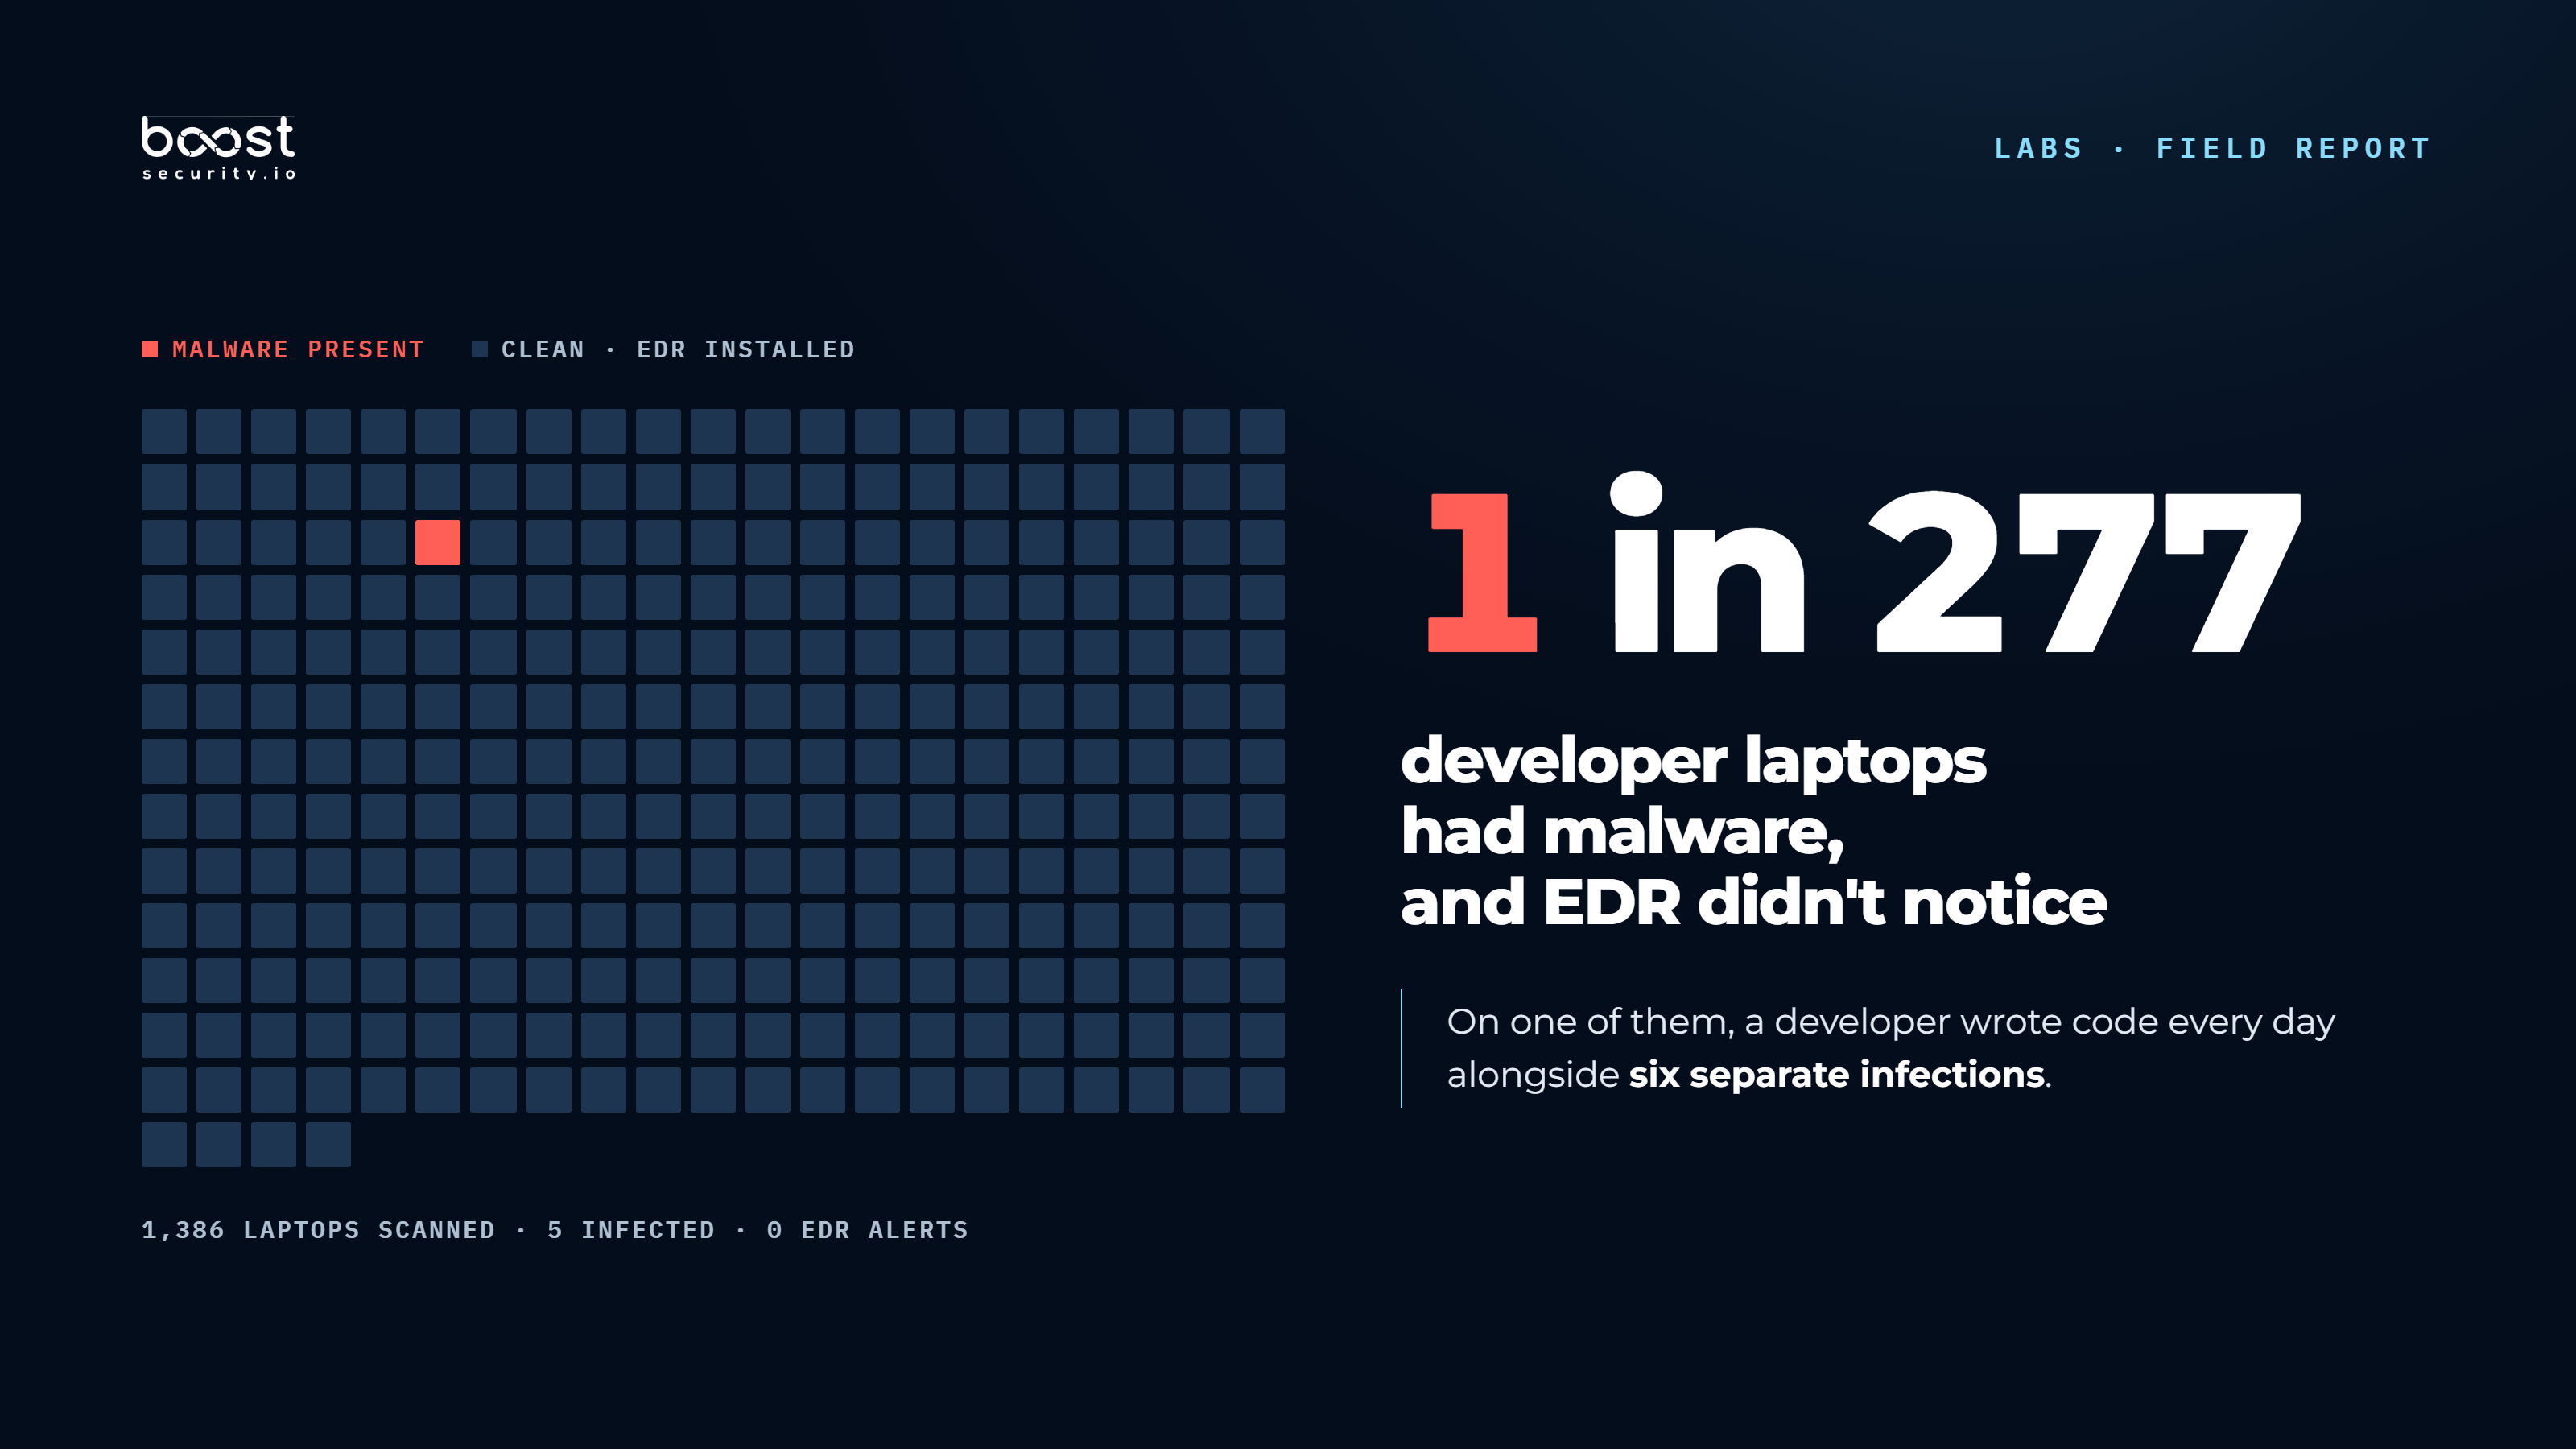
Blog ArticlesMalware on 1 in 277 Developer Laptops (And EDR Didn’t Notice)A scan of 1,386 developer laptops running commercial EDR found active malware on five of them, with no EDR alerts, plus 41,660 plaintext secrets the attackers could read. Here's what agentic coding tools add to that risk, and how to check your own laptop.October 13, 2026
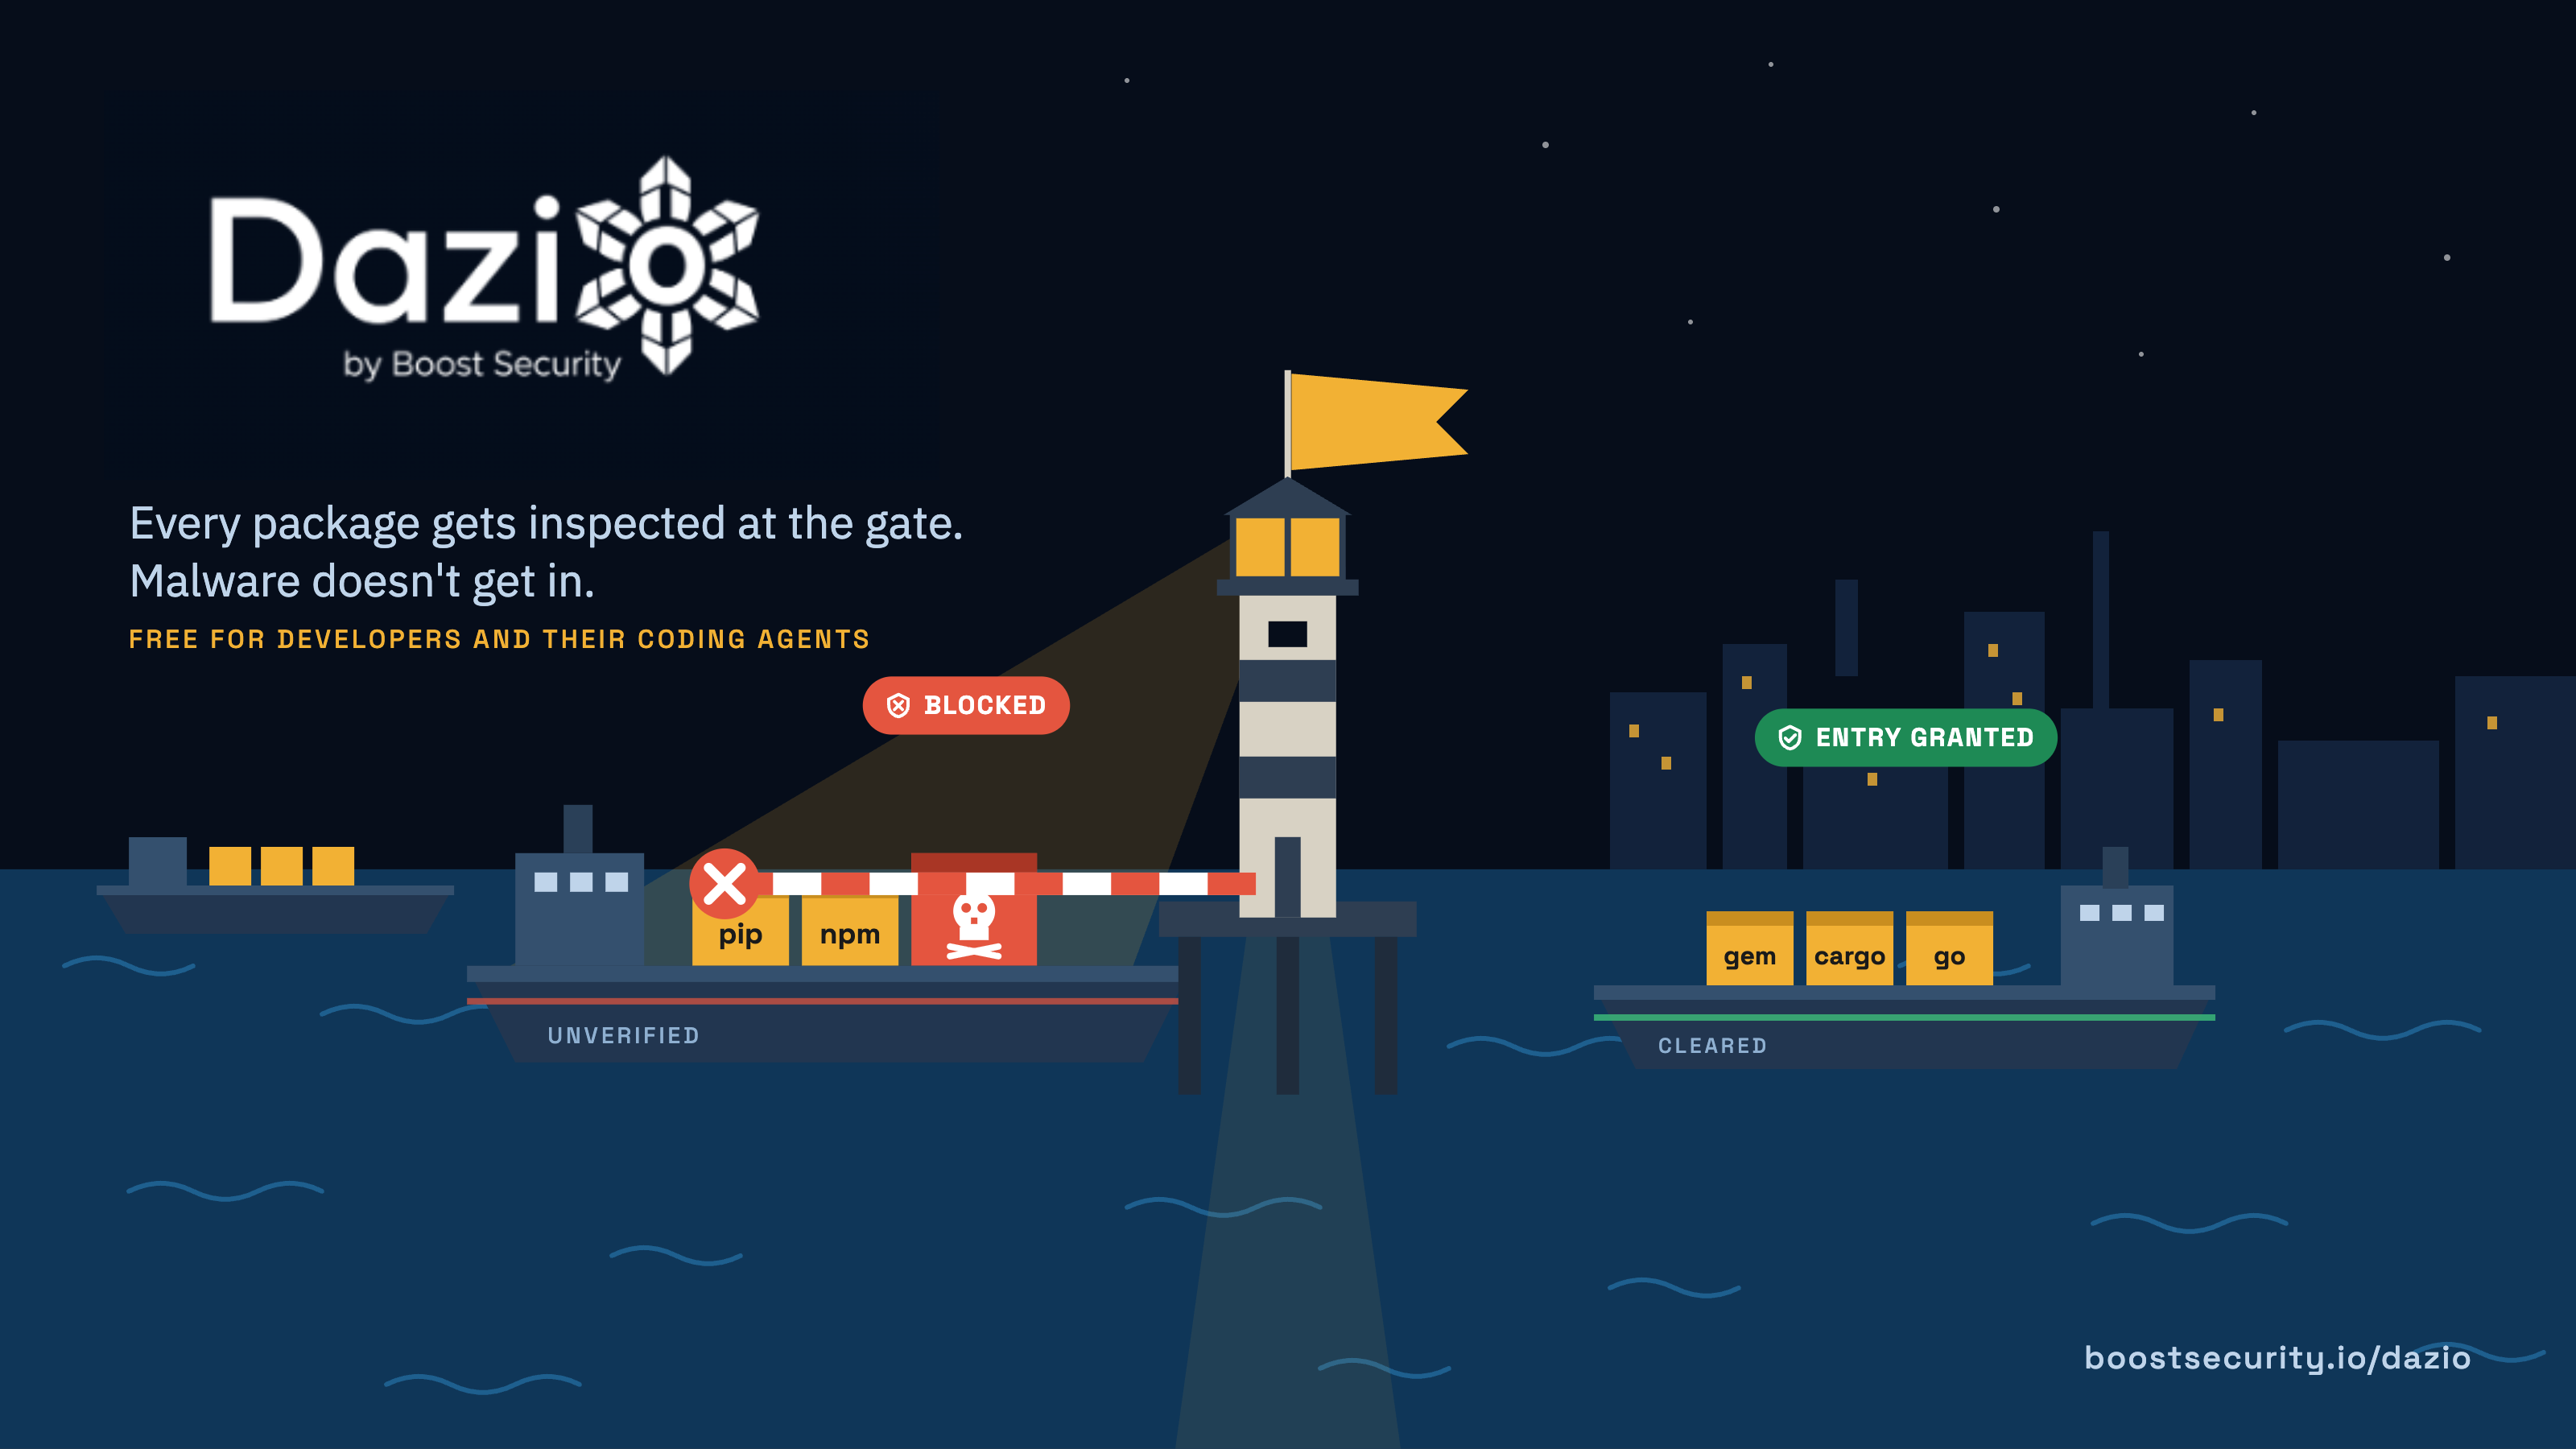
AppSecIntroducing DazioDazio is a free tool from BoostSecurity that protects developers and their coding agents against software supply chain attacks. It blocks malicious packages before they install, finds the ones already on your machine, cleans up the secrets attackers are after, and hardens the tools you and your agents build with.We built it because we think the world needs one. Software development got dramatically faster; the safety net did not keep up.October 2, 2026
Blog ArticlesWhat We Built This Summer at BoostSee what Boost shipped this summer across developer endpoints, ASPM, package security, scanning, access controls, and developer workflows.September 14, 2026
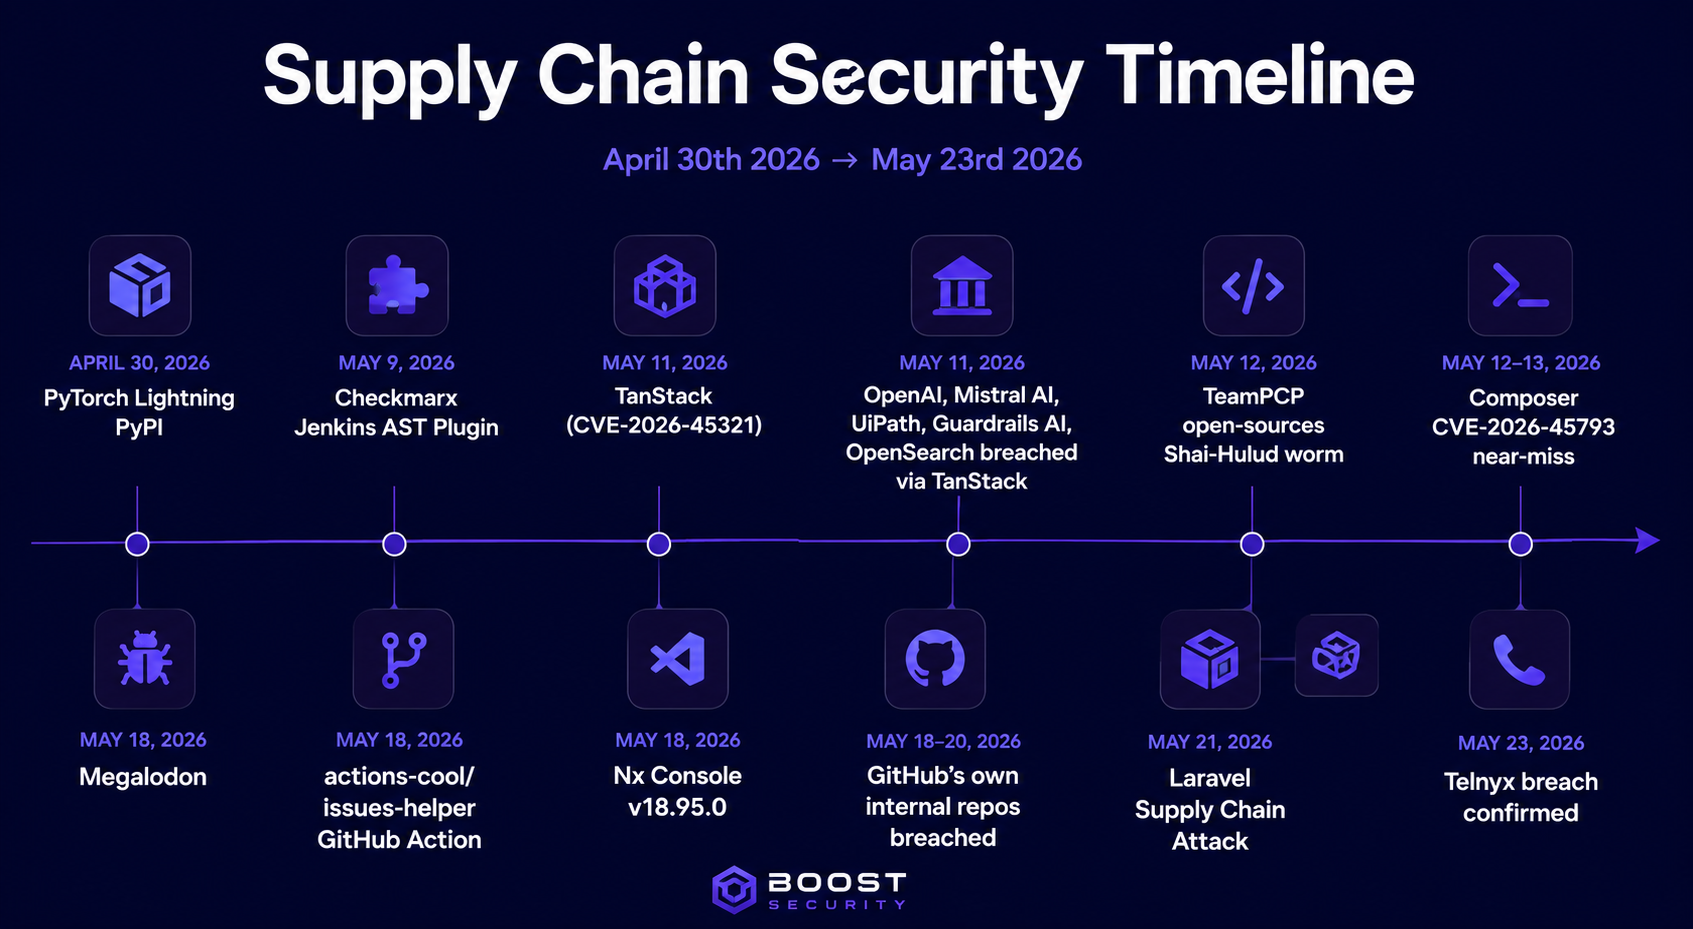
Blog ArticlesSupply Chain Hunting Season - May editionSoftware supply chain attacks are moving fast across developer endpoints, CI/CD pipelines, and open source ecosystems. Here’s what happened between April 30 and May 23—and what security teams should do about it.May 26, 2026
NewsAnnouncing two acquisitions and a funding round
Two acquisitions, one funding round, and a bigger platform: Boost adds Korbit.ai's AI-Native SAST and SecureIQx's reachability analysis to secure software factories running at machine speed.May 6, 2026

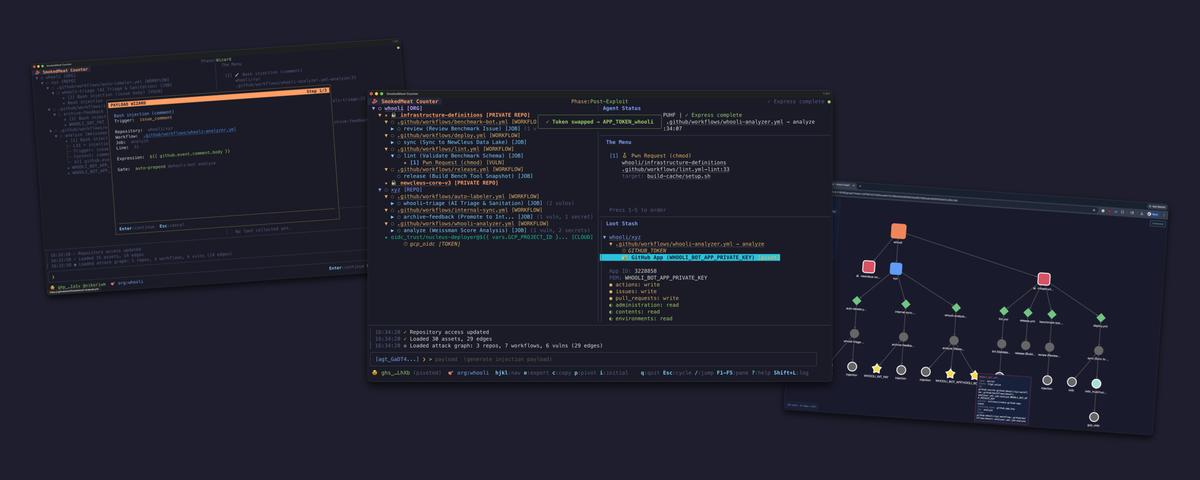
Blog ArticlesSmokedMeat: A Red Team Tool to Hack Your Pipelines FirstIn March 2026, TeamPCP unleashed mayhem on the software supply chain: compromising Trivy, LiteLLM, KICS, Telnyx, and dozens of npm packages, proving that CI/CD pipelines are the softest target. Today we're open-sourcing SmokedMeat, the first red team framework for build pipelines (i.e. CI/CD), so defenders can finally see the full kill chain for themselves.April 15, 2026
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Stay ahead of the threat.
Get the latest security research, pipeline attack analysis, and Boost product updates delivered to your inbox.