TL;DR
- About 45 open-source frameworks now automate attacks: Each one wires a language model into a loop that runs tools and acts on their output. We cataloged 32 of them into five families; the rest are forks and variants.
- Four ship a real secret scanner, but none ships the full pipeline: Pojun, Cybermes, Xalgorix, and AIRecon wire a scanner to the agent, yet none contains a GitHub fetcher. The model can assemble the rest at runtime, because each framework hands its agent a shell and web access.
- Dozens of operator consoles sit on the open internet: Of the 41 frameworks fingerprinted for Shodan, 11 serve a web UI by default. The ARTEX family alone matched 1,428 Shodan services on Nov. 7, 2026.
- The risk clusters in widely forked bases: It sits in a handful of heavily forked projects, not in the most-starred repositories.
ARTEX was one framework. The field around it holds about 45 more, each an open-source project that wires a language model into a loop that runs tools and acts on their output. We read the code and used Shodan to find every one accessible. Four ship a secret scanner wired to the agent by default. Dozens of operator consoles answered a Shodan query today. This post is the catalog: where each tool's code lives, what it ships for hunting secrets on public GitHub, and how it looks on the Internet.
ARTEX, briefly
ARTEX is an open-source agentic penetration-testing platform. Its creator took it down on 2026-10-08, 74 days after the first commit, following reports that threat actors were using it to hunt for secrets and move laterally with them. The takedown did not stop the spread: 102 forks and ARTEX-named repositories appeared in the takedown week alone. Google Threat Intelligence Group (GTIG), Microsoft, Wiz, CrowdStrike, Zscaler, Check Point, Censys, and RST Cloud have all written about ARTEX itself. This post covers the rest of the field.
ARTEX is not an isolated case. On Nov. 12, 2026, Palo Alto Networks Unit 42 reported a campaign of autonomous AI attacks built on a customized fork of Cairn, one of the frameworks in our catalog. In an autonomous AI attack, the operator supplies a target and a goal. The agent then plans and executes the intrusion and records the results on its own. Between August and September 2026, attackers ran 25 Cairn operations against at least 19 organizations and gained access or data at 10. One operation included a credential and secret collection phase, even though we found no secret-hunting capability in the public Cairn repository.
The 45 frameworks
Each framework has public source code and wires a model into a loop that runs tools and acts on their output. We cataloged 32 of the \~45 into five families, the remaining \~13 are forks, variants that reuse a family's pattern:
- Network kill chain. End-to-end recon, exploitation, and post-exploitation, usually from a Kali container. PentAGI runs agent teams with Nmap, Metasploit, and sqlmap. RedAmon builds an attack-surface graph. Xalgorix, Pentest-Swarm-AI, LuaN1aoAgent, AIRecon, redcell, PentestCode and cain-agent share the pattern. DarkMoon ships 50 specialist agents across web, cloud, Active Directory, and CI/CD.
- Web-app and API. Strix tests web applications autonomously. Shannon works from source code, closer to a SAST reviewer than a live kill chain. PentestGPT is an advisory assistant. T3MP3ST, Apex, deadend-cli and PentesterFlow sit nearby.
- C2-integrated. Sage and echidna run as LLM operators inside the Mythic C2 framework. virga puts a local model inside the implant. Pojun and FORANG are ARTEX derivatives that bolt a C2 console onto the base, so they belong here rather than in the kill-chain family; ycode is a third ARTEX derivative, and ScopeWeaver is an English- and Korean-localized fork of ARTEX.
- Harnesses. RAPTOR, CyberStrike, cyber-harness, Nebula and Cybermes wrap a general coding agent (Claude Code, Codex, Hermes) with offensive skills. Plugin packs do the same for coding agents; we track those as one group.
- Research prototypes. Incalmo, hackingBuddyGPT, VulnBot, HackSynth, AutoPT and Ares come out of academic work.
Three more appear in threat reporting and are worth including. Cairn coordinates worker agents on a shared fact graph, with no authentication by default. HexStrike is an MCP server that exposes more than 150 offensive tools to any MCP client, with no authentication by default. Agent Zero is a general-purpose agent, also with no authentication by default, that threat actors have experimented with. CAI was archived on 2026-08-28.
The 13 last frameworks that couldn’t be included in any family are variants, forks, and research seeds that share a family's pattern.
The catalog below gives one row per tool: where the code lives, how popular and how active it is, what it ships for secret-hunting, and how visible it is on Shodan. Stars and last-push are from the GitHub API on 2026-11-07. "Not reviewed" means the tool was outside the secret-hunting shortlist, so we did not inspect it: not the same as "None found," where we read the code and found no secret-hunting capability. Section 2 defines the shortlist and full grade scale.
Secret-hunting grades, in short: Provisioned (scanner named, reachable by the agent), Text only (recipe or skill, no scanner), Unwired (scanner named, nothing calls it), None found (reviewed, nothing there), Not reviewed (outside the shortlist). Section 2 explains each.
What ships for hunting secrets
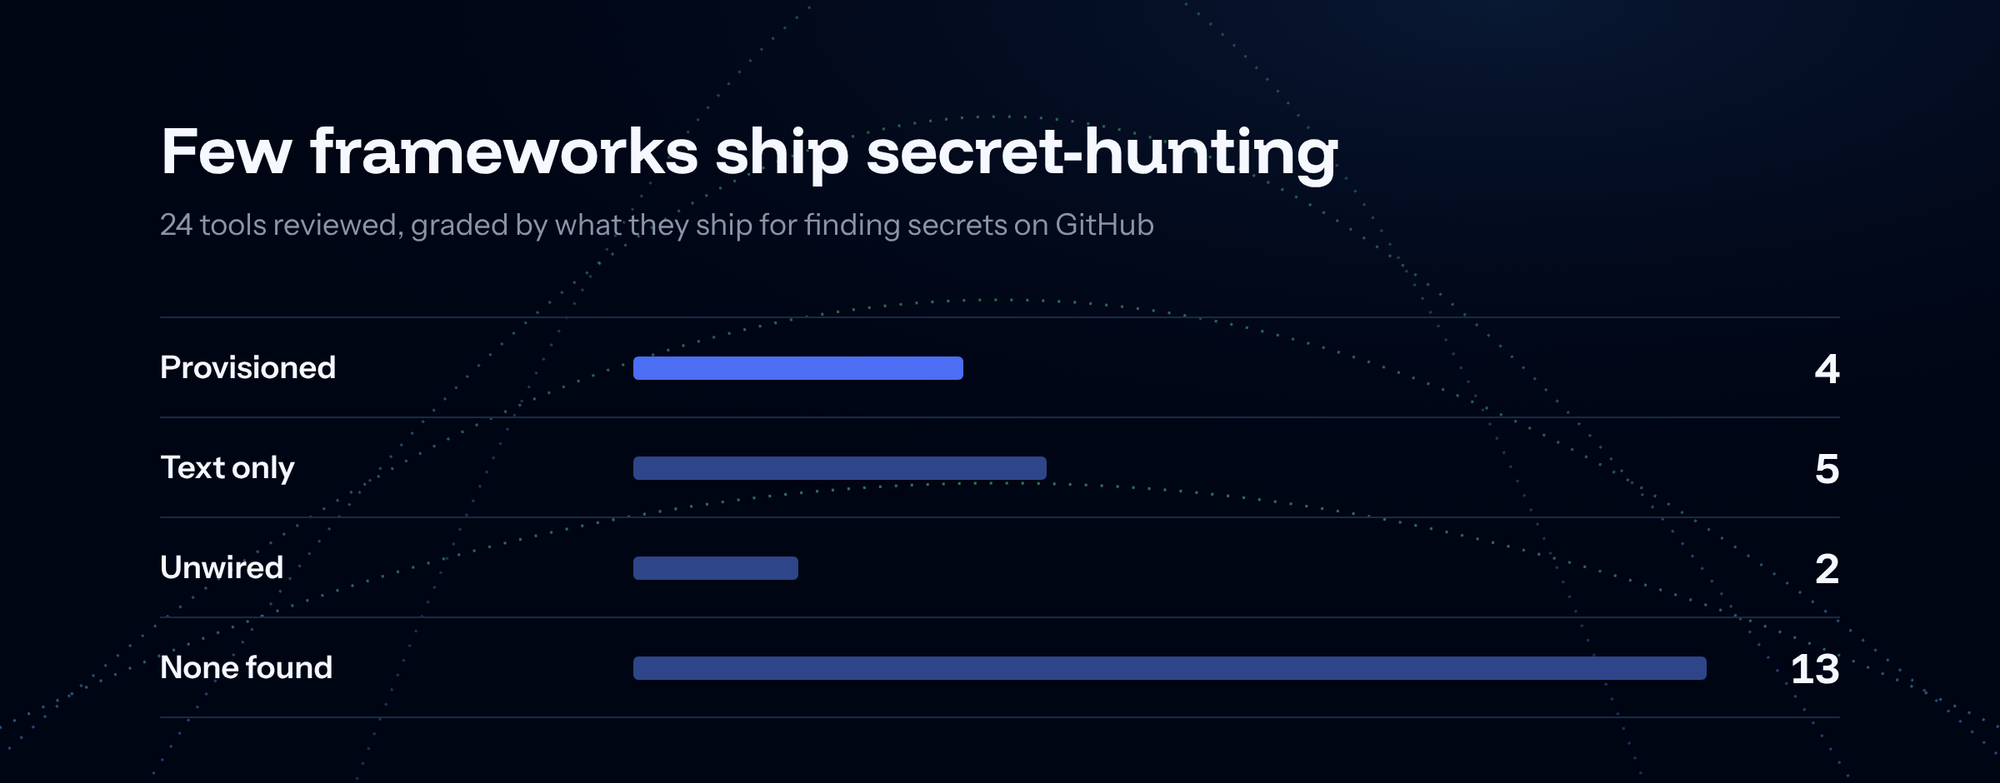
We shortlisted the tools most likely to ship secret-hunting (the ARTEX forks, the Kali-container network agents, and the harnesses with OSINT skills) and read each at a pinned commit, grading what it ships for finding secrets on public GitHub.
- Provisioned: a scanner is named in the code, and GitHub guidance reaches the agent by default.
- Text only: recipes or skills, but no scanner the agent can run.
- Unwired: code present, but no agent can call it.
- None found: reviewed, nothing present.
Four tools ship a real scanner wired to the agent: Pojun, Cybermes, Xalgorix and AIRecon. None contains a GitHub fetcher. Almost every framework in the catalog hands its agent a shell and web access, so a GitHub search or a scanner download is one improvised tool call away. A model and a prompt supply the capability. The repository does not ship it.
What they look like on Shodan
Shodan indexes services, so the first question is whether a framework exposes anything to match. We classified each from its code. Of the \~45 frameworks, 41 are fingerprint-assessed for Shodan ; 11 serve a web UI on a network port by default, 18 serve a UI only in some setups or nothing distinctive at the root, and 12 have no listener at all. We wrote 56 fingerprint records, one per build with a distinct web interface.
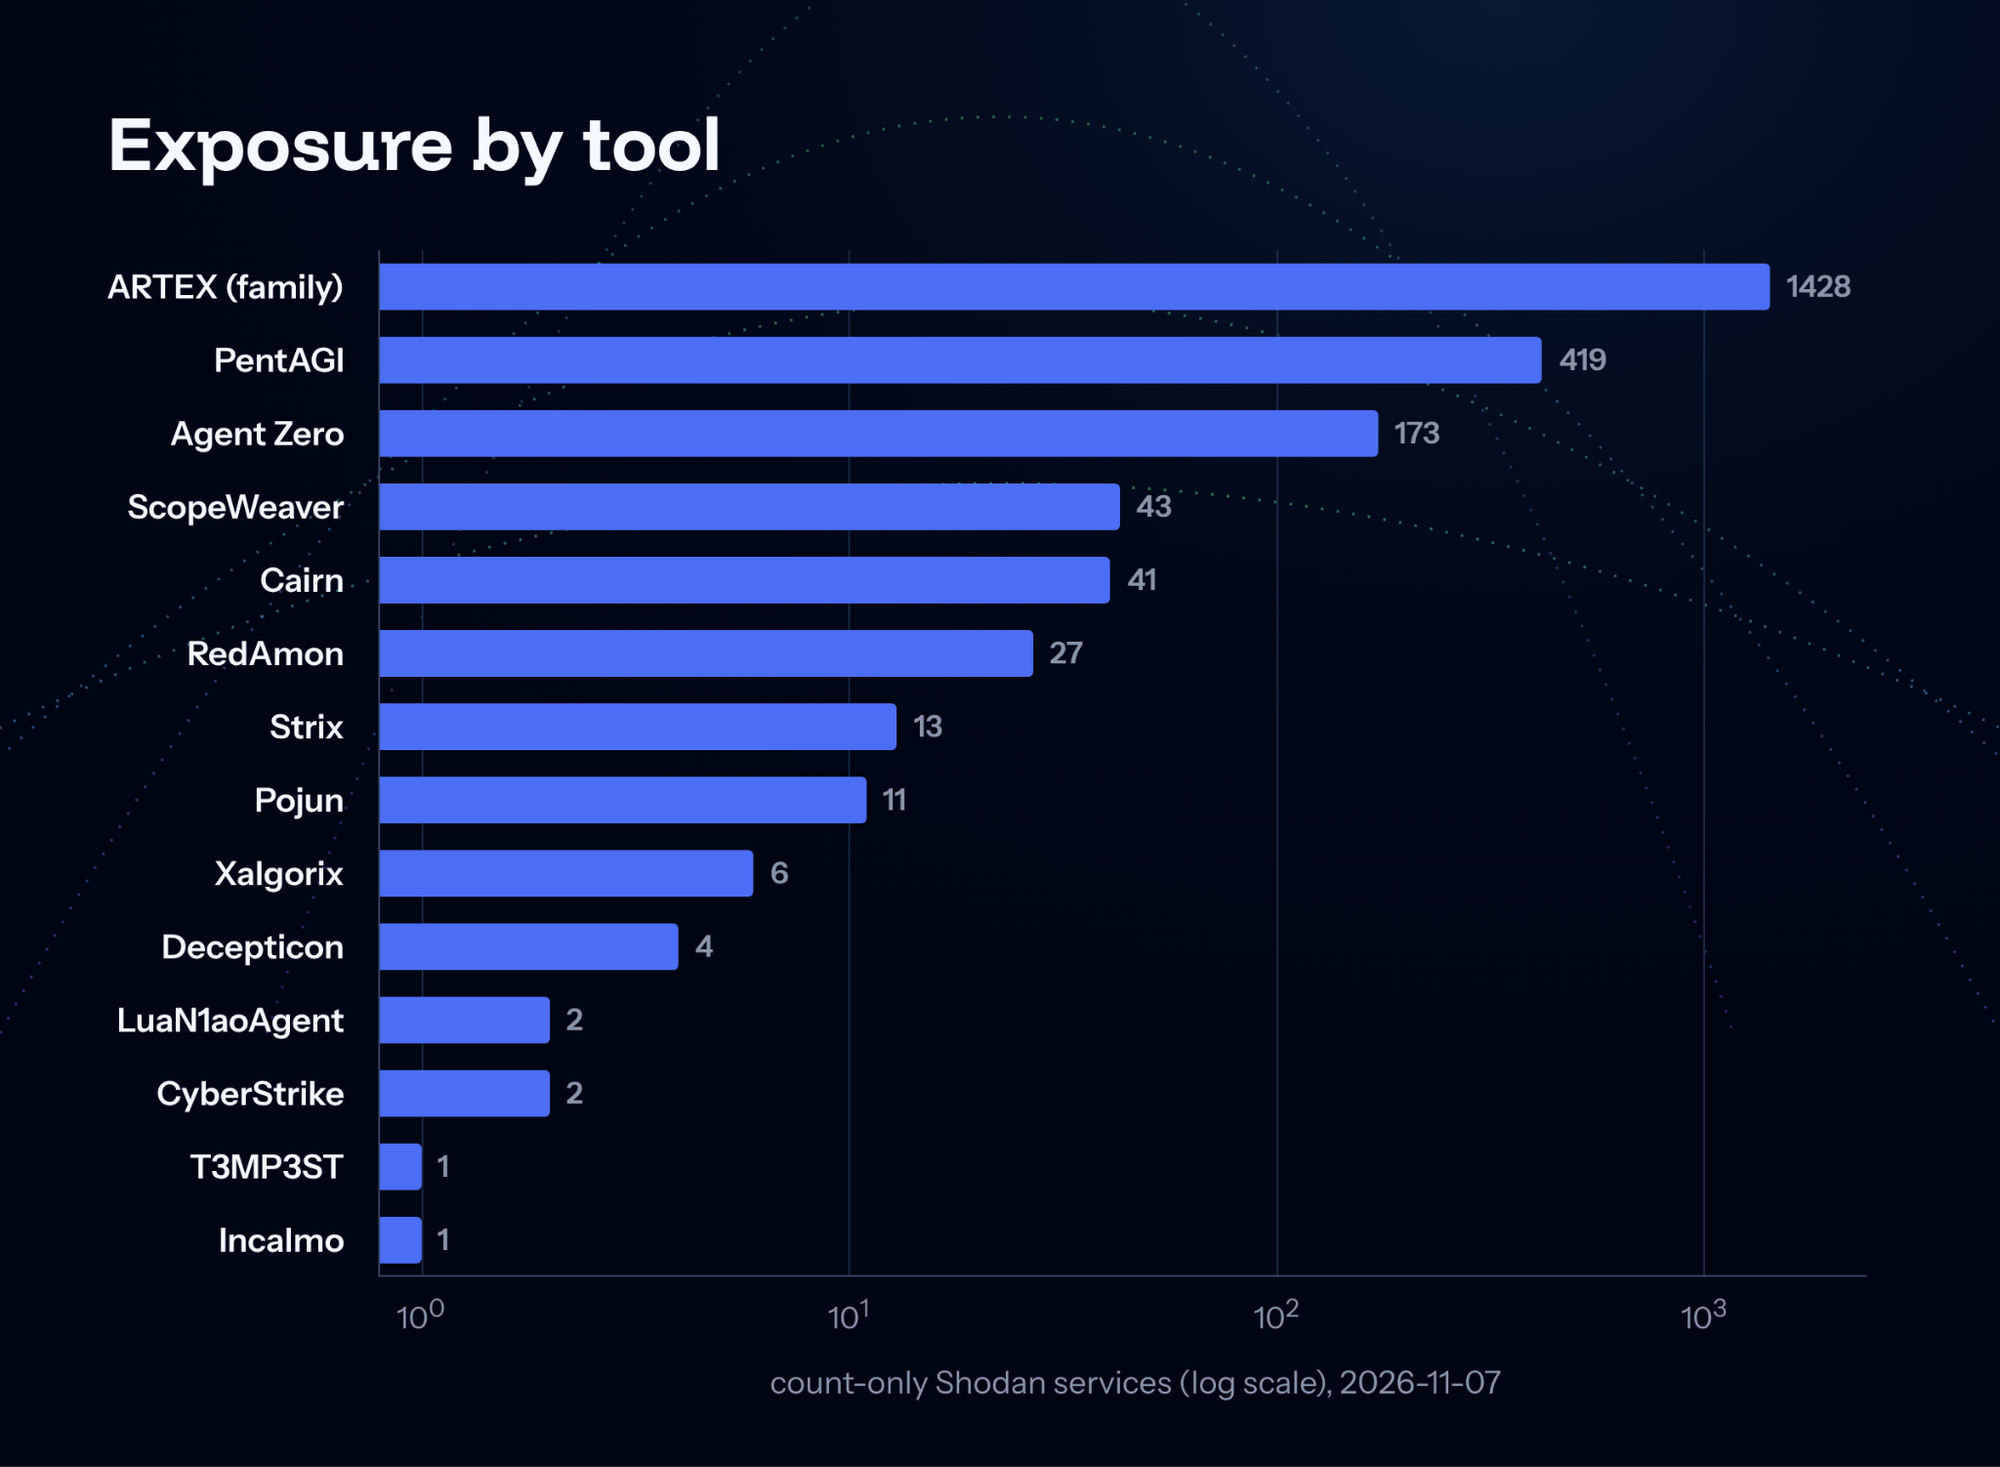
Figure: count-only Shodan services per tool on 2026-11-07, log scale, led by the ARTEX family at 1,428
What to take from this
Forty-five frameworks, but the risk clusters in a handful of widely forked bases, not in the most-starred repositories.
Almost none of these tools ship a secret-hunting pipeline, but that is no comfort. Each hands its agent a shell and web access, so the model can assemble one at runtime. A GitHub search, a scanner download, a found key passed to the next call: all one prompt away, none of it shipped in the repo.
Dozens of operator consoles answered a Shodan query on our scan date, many behind no real barrier. We publish fingerprint descriptions, not a target list, so defenders can find their own exposed instances first.
Hunting queries
The following table summarizes the Shodan queries we used to match the live tools' public instances
ARTEX is just one of many tools that hunt for exposed secrets. Do you know what they'd find? Run a free GitHub Security Audit to see which credentials linked to your organization are already exposed on public GitHub.
Check your exposure on public GitHub
FAQ
What are agentic AI pentesting tools?
Agentic AI pentesting tools are open-source projects that wire a language model into a loop that runs tools and acts on their output. About 45 exist. GitGuardian cataloged 32 of them into five families: network kill chain, web app and API, command-and-control (C2) integrated, harnesses, and research prototypes. The rest are forks and variants that reuse a family’s pattern.
What is an autonomous AI for cyber attacks?
An autonomous AI for cyber attacks is a self-sufficient system that can independently plan, execute, and adapt complex cyber intrusions with little to no human involvement. Unlike traditional methods, where a human takes the reins and uses AI to generate code or craft phishing emails, this kind of AI operates on its own. It analyzes the environment, makes tactical decisions in real time, and can quickly change its strategy if it encounters any defenses. Essentially, it's like having a digital strategist that can outsmart obstacles on its own.
Do agentic AI pentesting tools hunt for secrets on GitHub?
Agentic AI pentesting tools rarely ship secret-hunting on their own. Four ship a real scanner wired to the agent: Pojun, Cybermes, Xalgorix, and AIRecon. None of them contains a GitHub fetcher.
Why do agentic AI pentesting tools still matter if they don’t ship a secret-hunting pipeline?
Agentic AI pentesting tools hand their agent a shell and web access, so the model can assemble a pipeline at runtime. A GitHub search, a scanner download, and a found key passed to the next call are all one prompt away, even though none of it ships in the repository.
How many ARTEX consoles are exposed on Shodan?
ARTEX consoles matched 1,428 count-only Shodan services on Nov. 7, 2026, the most of any tool in the catalog. PentAGI followed with 419 and Agent Zero with 173.
How do you find exposed agentic AI pentesting tools on Shodan?
Agentic AI pentesting tools are found on Shodan with fingerprints that match a page title, favicon hash, page HTML, or TLS certificate. Of the 41 frameworks assessed, 11 serve a web UI by default, 18 serve one only in some setups or show nothing distinctive at the root, and 12 have no listener at all. GitGuardian wrote 56 fingerprint records, one per build with a distinct web interface.
Are exposed agentic AI pentesting consoles protected?
Exposed agentic AI pentesting consoles are often not protected. Dozens answered a Shodan query on the scan date, many behind no real barrier. Of the 173 Agent Zero services found, 134 sat at a login and 39 were open.