Modern security operations leave exploitable gaps
Expanding attack surfaces, disconnected tools, and limited context make it harder for teams to detect threats and respond at scale.

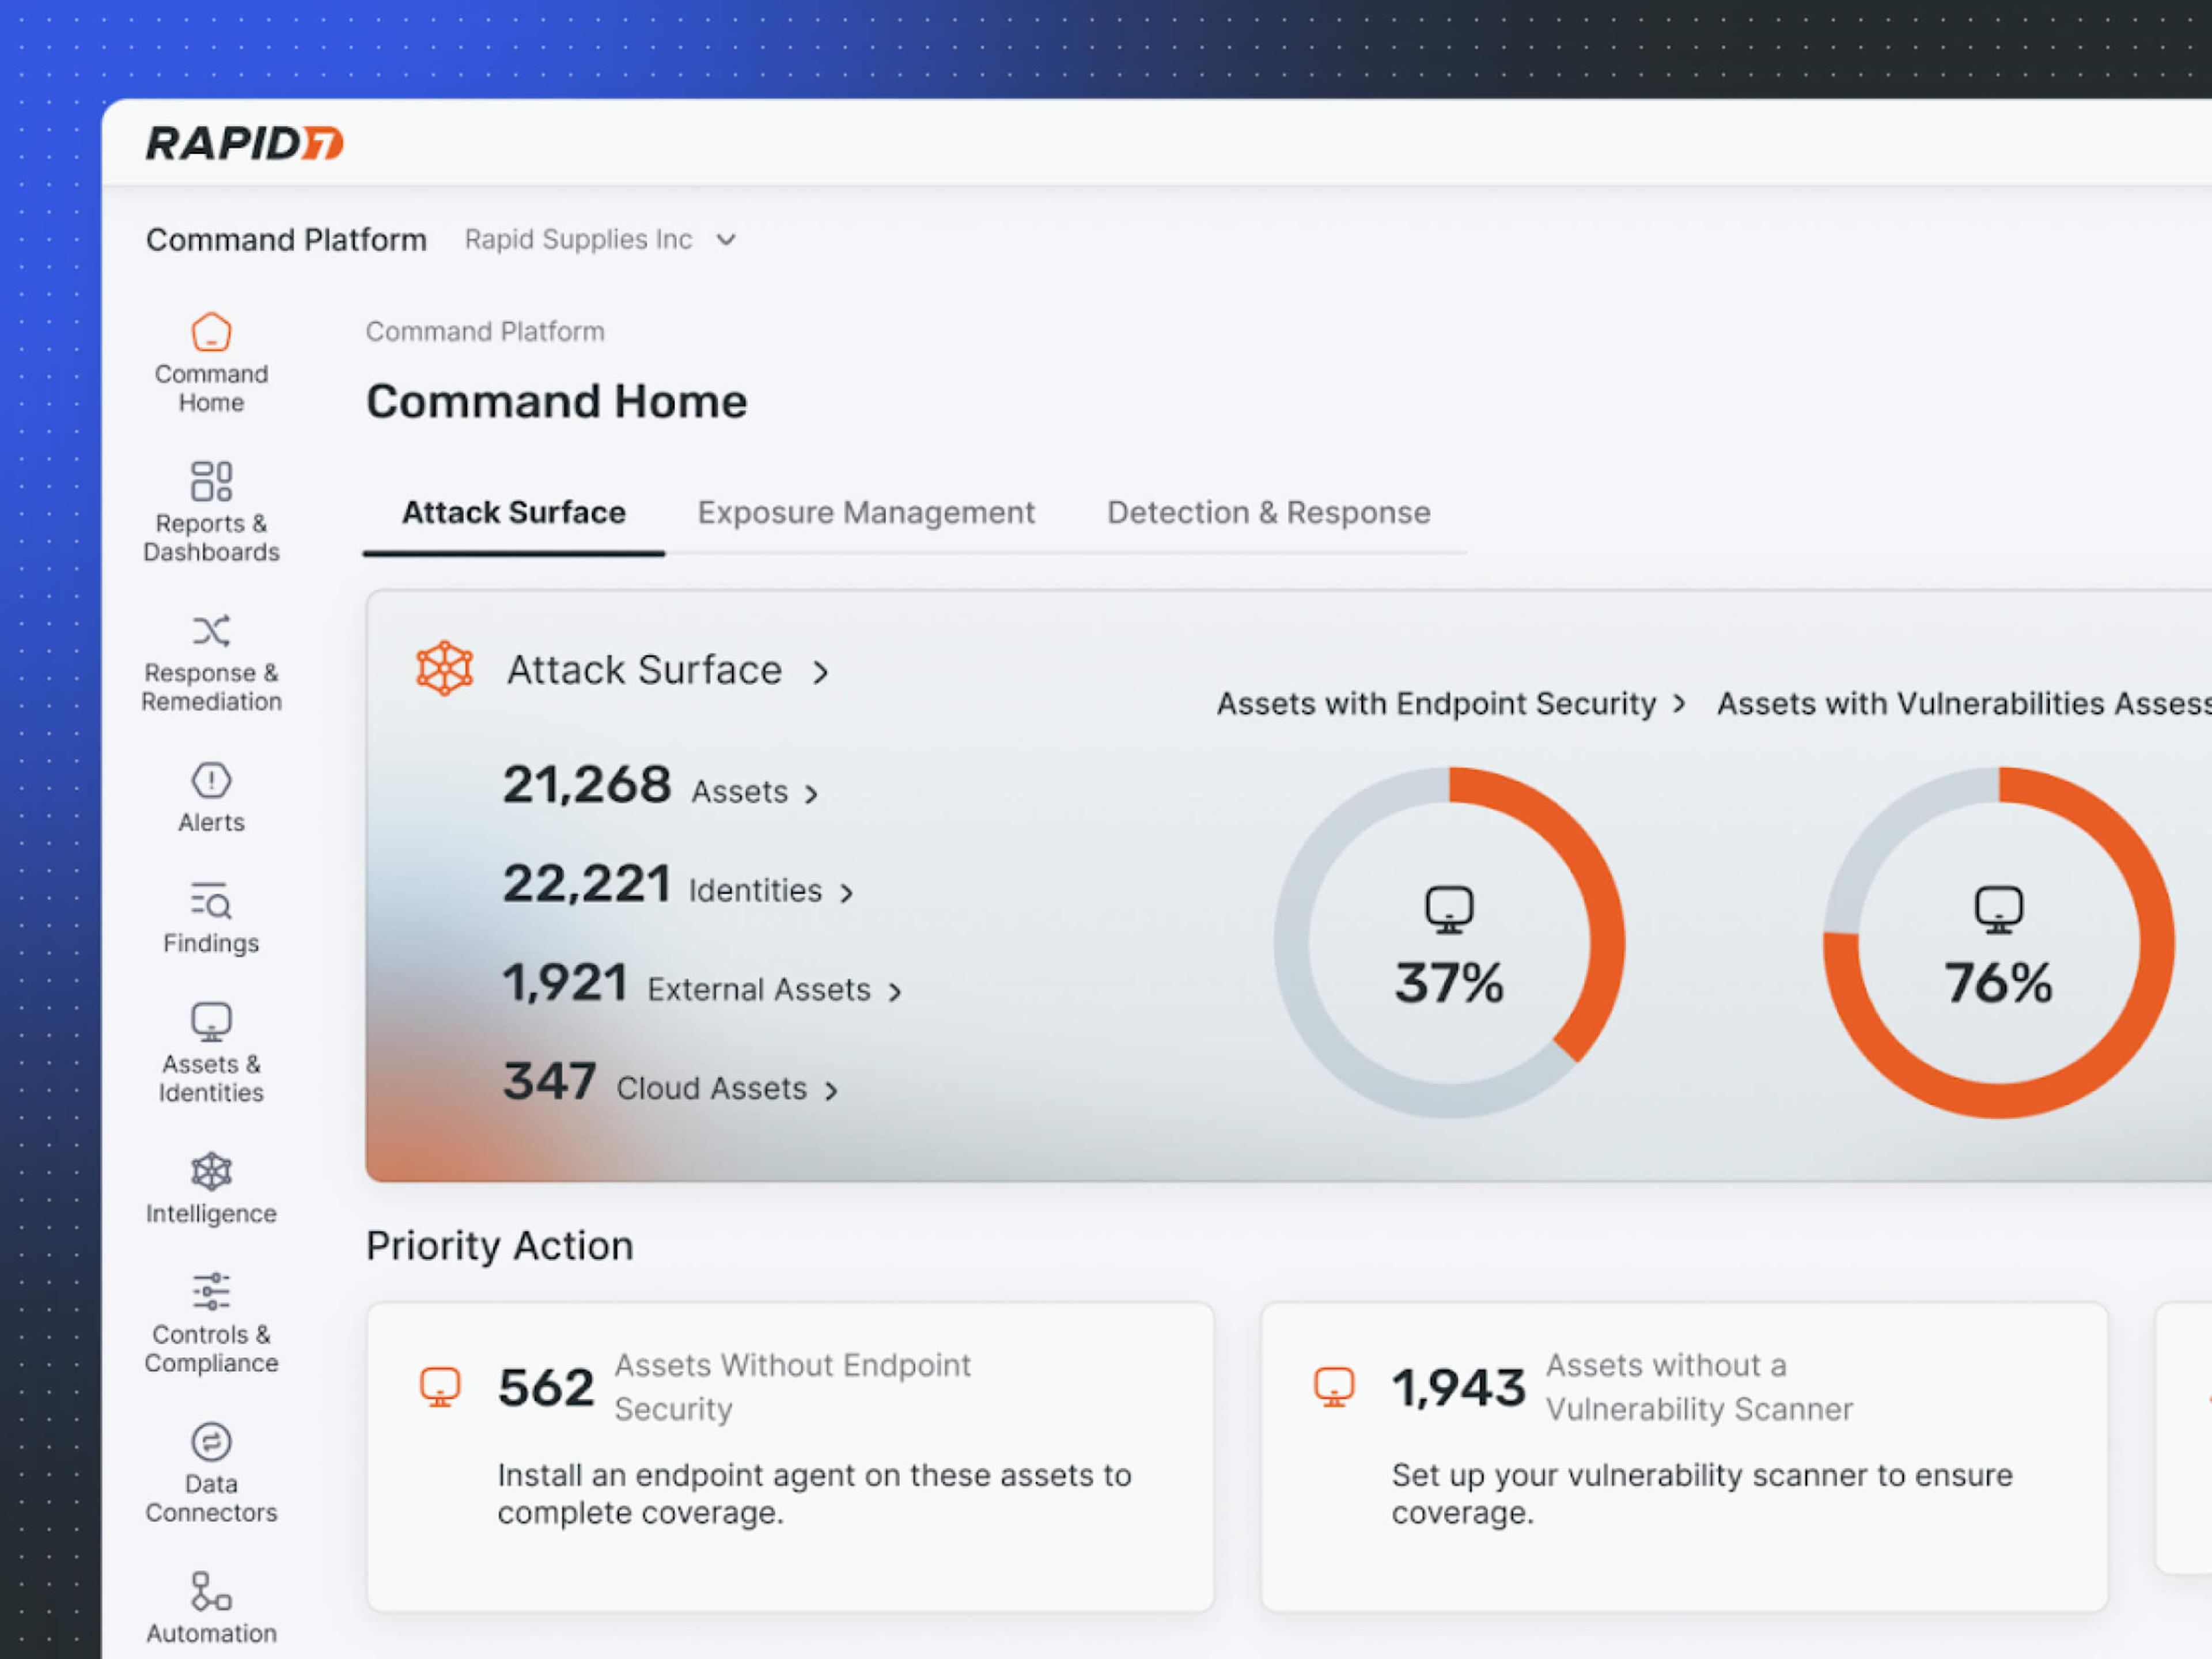
Attack surface gaps create blind spots
Cloud, identity, endpoint, SaaS, and unmanaged assets expand the attack surface and create gaps attackers can exploit.

Missing context slows SOC action
When alerts lack asset, user, risk, and threat context, analysts spend time stitching signals together instead of responding.

Manual security operations don’t scale
Growing alert volume and fragmented workflows make it harder to investigate consistently, reduce noise, and respond faster.
Attack surface gaps create blind spots
Cloud, identity, endpoint, SaaS, and unmanaged assets expand the attack surface and create gaps attackers can exploit.
Missing context slows SOC action
When alerts lack asset, user, risk, and threat context, analysts spend time stitching signals together instead of responding.
Manual security operations don’t scale
Growing alert volume and fragmented workflows make it harder to investigate consistently, reduce noise, and respond faster.
AI-powered capabilities for modern SOCs
Unify detection, investigation, and response to detect threats instantly, investigate clearly, and act with confidence to stop threats faster.
Threat Intelligence
Act on relevant threats faster
Use curated threat intelligence to understand which threats matter, connect campaigns and IOCs to investigations, and prioritize action with confidence.

Choose the path that fits your team
AI-powered detection and response, fit for your team’s needs.

Integrations
Resources
Managed Threat Complete BriefPreemptive MDRRead
Incident Command BriefAI-native SIEMRead
Rapid7 AI EngineAI-driven protectionExplore
Managed Threat Complete BriefPreemptive MDRRead
Incident Command BriefAI-native SIEMRead
Rapid7 AI EngineAI-driven protectionExplore
Frequently asked questions
Take command of security operations
See how AI-powered security operations help your team cut noise, investigate faster, and respond with more confidence.